Home Blog Page 6

Blockchain Enterprise Adoption 2025: Stablecoins Process $9 Trillion as Real-World Use Cases Emerge

0
Blockchain Enterprise Adoption 2025: Stablecoins Process  Trillion as Real-World Use Cases Emerge

Table of Contents

    Bitcoin cryptocurrency coins representing blockchain technology and enterprise digital asset adoption

    Photo by David McBee via Pexels

    Introduction: Blockchain’s Enterprise Breakthrough Year

    Stablecoins processed $9 trillion in payments in 2025, an 87% jump from 2024. September alone hit $1.25 trillion. These striking numbers signal blockchain moving from speculation to practical enterprise adoption. McKinsey research suggests tokenized cash and stablecoins could drive the next generation of payments, marking 2025 as a pivotal year for enterprise blockchain adoption.

    Stablecoin Surge: The Killer App for Blockchain Payments

    2025 Stablecoin Statistics

    • Total Volume: $9 trillion processed
    • Growth Rate: 87% year-over-year
    • September 2025: $1.25 trillion single-month volume
    • Use Cases: Cross-border payments, remittances, B2B settlements

    Why Stablecoins Are Winning

    Advantages Over Traditional Payment Rails:
    • Speed: Near-instant settlement vs. days for traditional banking
    • Cost: Significantly lower fees than wire transfers or card payments
    • Accessibility: 24/7 operation vs. banking hours
    • Programmability: Smart contract integration enabling automation
    • Transparency: Blockchain-based audit trails
    Enterprise Use Cases:
    • Cross-border B2B payments
    • Supply chain finance
    • Payroll for international contractors
    • Treasury management and cash positioning

    Enterprise Blockchain Adoption: Beyond Cryptocurrency

    1. Supply Chain and Logistics

    Applications:
    • Product provenance and authenticity verification
    • Shipment tracking and documentation
    • Automated customs and compliance
    • Supplier verification and credentials
    Benefits: Transparency, traceability, reduced fraud, efficiency.

    2. Trade Finance and Banking

    Applications:
    • Letters of credit digitization
    • Trade documentation on blockchain
    • Settlement and clearing systems
    • Identity verification (KYC/AML)
    Players: JPMorgan’s Onyx, HSBC, Standard Chartered, others.

    3. Tokenization of Real-World Assets

    Assets Being Tokenized:
    • Real estate investment and fractional ownership
    • Commodities (gold, oil, agricultural products)
    • Corporate bonds and securities
    • Art and collectibles
    Value Proposition: Increased liquidity, fractional ownership, 24/7 markets, programmable assets.

    4. Healthcare and Pharmaceuticals

    Applications:
    • Drug supply chain verification (anti-counterfeiting)
    • Medical records management and interoperability
    • Clinical trial data integrity
    • Insurance claims processing automation

    Blockchain Technology Evolution in 2025

    Scalability Improvements

    • Layer-2 scaling solutions maturing
    • Sharding implementations increasing throughput
    • Optimized consensus mechanisms
    • Cross-chain interoperability advancing

    Enterprise-Grade Features

    • Permissioned blockchain platforms
    • Privacy-preserving technologies (zero-knowledge proofs)
    • Regulatory compliance built-in
    • Integration with existing enterprise systems

    Barriers to Blockchain Adoption

    Challenges Remaining:
    1. Regulatory Uncertainty: Evolving frameworks create compliance complexity
    2. Interoperability: Different blockchain platforms don’t communicate easily
    3. Scalability: Many blockchains still limited in transaction throughput
    4. Energy Consumption: Proof-of-work chains face environmental concerns
    5. Talent Shortage: Limited blockchain expertise
    6. Integration Complexity: Connecting blockchain to legacy systems

    Why 2025 May Be Blockchain’s Inflection Point

    Convergence of Factors:
    • Stablecoin adoption proving real-world utility
    • Enterprise platforms maturing
    • Regulatory frameworks emerging (MiCA in EU)
    • Integration tools and platforms improving
    • Executive understanding and acceptance growing
    Market Signal: Polkadot as only blockchain sponsor at TechCrunch Disrupt 2025 with nearly 10,000 booth visitors shows enterprise interest.

    Strategic Recommendations

    For Enterprises Considering Blockchain

    1. Focus on narrow, high-impact use cases
    2. Pilot before full deployment
    3. Partner with established blockchain platforms
    4. Address regulatory compliance upfront
    5. Build internal blockchain literacy

    For Blockchain Vendors

    1. Prioritize enterprise integration capabilities
    2. Provide regulatory compliance support
    3. Focus on solving real business problems
    4. Demonstrate ROI with case studies

    Conclusion: From Hype to Reality

    Blockchain in 2025 represents transition from cryptocurrency speculation to practical enterprise tool. Stablecoin payment volume growth and real-world asset tokenization demonstrate genuine utility. The Quiet Revolution: Enterprise blockchain adoption accelerating not through universal platforms but through narrow, high-impact specialized workflows. Organizations should evaluate blockchain for specific use cases where its unique properties (transparency, immutability, decentralization) solve real problems.

    Sources: Forbes, PYMNTS, McKinsey, Senior Executive, LinkedIn, Polkadot, Global Blockchain Show

    blockchain enterprise adoption 2025 - overview of blockchain enterprise adoption 2025 concepts and framework
    blockchain enterprise adoption 2025 - blockchain enterprise adoption 2025 implementation and architecture diagram
    blockchain enterprise adoption 2025 - blockchain enterprise adoption 2025 statistics and key metrics visualization

    The State of Blockchain Enterprise Adoption 2025

    Blockchain enterprise adoption 2025 has reached an inflection point. What began as cryptocurrency infrastructure has evolved into a foundational technology transforming how businesses handle payments, supply chains, identity, and data integrity across industries.

    The numbers tell a compelling story. Blockchain enterprise adoption 2025 metrics show stablecoin transaction volumes exceeding $9 trillion annually, with Fortune 500 companies running production blockchain workloads at unprecedented scale.

    Stablecoins Driving Blockchain Enterprise Adoption 2025

    The $9 Trillion Milestone

    Stablecoins represent the most visible success of blockchain enterprise adoption 2025. Processing $9 trillion in annual transactions, stablecoins have become legitimate enterprise payment infrastructure rather than speculative crypto instruments.

    Major corporations now use stablecoins for cross-border payments, supplier settlements, and treasury management. The blockchain enterprise adoption 2025 trend shows businesses saving significantly on transaction fees and settlement times compared to traditional banking rails.

    Regulatory clarity in key jurisdictions accelerated this adoption. The blockchain enterprise adoption 2025 framework benefited from stablecoin legislation in the US, EU’s MiCA regulation, and Singapore’s progressive licensing approach, giving enterprises confidence to deploy at scale.

    Payment Infrastructure Transformation

    Beyond stablecoins, broader payment infrastructure transformation defines blockchain enterprise adoption 2025. Central bank digital currency pilots progressed in over 130 countries, with several moving from pilot to production.

    Enterprise payment platforms integrated blockchain settlement layers, enabling instant, programmable money movement. The blockchain enterprise adoption 2025 landscape now includes blockchain-based payroll systems, automated escrow services, and programmable insurance payouts.

    Supply Chain: Blockchain Enterprise Adoption 2025

    Provenance and Traceability

    Supply chain management remains a primary blockchain enterprise adoption 2025 use case. Major retailers, food producers, and pharmaceutical companies use blockchain to track products from origin to consumer, ensuring authenticity and compliance.

    Walmart’s food traceability system, expanded significantly in 2025, represents a benchmark blockchain enterprise adoption 2025 case study. The system reduces foodborne illness investigation time from days to seconds by providing immutable supply chain records.

    Pharmaceutical supply chains leverage blockchain for anti-counterfeiting and cold chain verification. Blockchain enterprise adoption 2025 in pharma addresses regulatory requirements like the US Drug Supply Chain Security Act through tamper-evident tracking.

    Trade Finance Modernization

    Trade finance, traditionally paper-heavy and slow, transformed through blockchain enterprise adoption 2025. Platforms like Marco Polo and Contour enabled digitized letter of credit processes, reducing settlement times from weeks to days.

    Major banks reported significant efficiency gains. The blockchain enterprise adoption 2025 impact on trade finance includes reduced documentation costs, fewer disputes, and improved working capital cycles for participating businesses.

    Identity Management: Blockchain Enterprise Adoption 2025

    Decentralized Identity

    Self-sovereign identity systems gained substantial traction in blockchain enterprise adoption 2025. Governments and enterprises deployed decentralized identity solutions giving users control over personal data while reducing identity fraud.

    The European Digital Identity Wallet, incorporating blockchain verification, represents a landmark blockchain enterprise adoption 2025 initiative. It enables citizens to authenticate identity across services without centralized data stores vulnerable to breaches.

    Enterprise applications include employee credential verification, B2B partner authentication, and customer KYC processes. Blockchain enterprise adoption 2025 identity solutions reduce onboarding friction while improving security and privacy.

    Real-World Use Cases in Blockchain Enterprise Adoption 2025

    Healthcare Data Management

    Healthcare emerged as a significant blockchain enterprise adoption 2025 sector. Medical record sharing, clinical trial data integrity, and pharmaceutical supply tracking all benefited from blockchain’s tamper-evident architecture.

    Several health systems deployed blockchain for patient consent management, giving patients granular control over who accesses their records. The blockchain enterprise adoption 2025 healthcare use cases address long-standing interoperability and trust challenges.

    Real Estate and Tokenization

    Asset tokenization represents a rapidly growing blockchain enterprise adoption 2025 category. Real estate, fine art, and intellectual property tokenization opened new investment access and liquidity for traditionally illiquid assets.

    Property transactions on blockchain reduced intermediary costs and accelerated closing times. Blockchain enterprise adoption 2025 tokenization platforms processed billions in real estate value, demonstrating mainstream acceptance.

    Energy and Carbon Credits

    Energy trading and carbon credit tracking benefited from blockchain enterprise adoption 2025. Peer-to-peer energy trading platforms enabled direct transactions between producers and consumers, while carbon credit registries on blockchain prevented double-counting.

    Major energy companies adopted blockchain for renewable energy certificate management. The blockchain enterprise adoption 2025 environmental applications help organizations meet ESG goals with verifiable, auditable data.

    Technical Evolution Supporting Blockchain Enterprise Adoption 2025

    Scalability Solutions

    Layer 2 scaling solutions matured significantly, addressing the throughput limitations that previously hindered blockchain enterprise adoption 2025. Rollups, state channels, and app-specific chains enabled enterprise-grade transaction volumes.

    Ethereum’s Layer 2 ecosystem processed more transactions than the main chain, with fees low enough for micro-transactions. This blockchain enterprise adoption 2025 enabler made blockchain economically viable for high-frequency business applications.

    Interoperability

    Cross-chain communication protocols improved, allowing different blockchain networks to exchange data and value. Blockchain enterprise adoption 2025 benefited from interoperability standards reducing vendor lock-in concerns.

    Enterprise blockchain platforms developed bridges to public networks, enabling hybrid architectures combining private permissioned chains with public verification. This blockchain enterprise adoption 2025 architectural pattern balances privacy with transparency.

    Privacy and Compliance

    Zero-knowledge proofs became production-ready for enterprise use, enabling blockchain enterprise adoption 2025 applications that prove data validity without revealing the data itself. This addressed privacy concerns that previously slowed adoption.

    Compliance tooling integrated with blockchain platforms, helping organizations meet regulatory obligations while leveraging distributed ledger benefits. The blockchain enterprise adoption 2025 compliance landscape matured with audit trail standards and regulatory reporting integrations.

    Challenges in Blockchain Enterprise Adoption 2025

    Despite progress, blockchain enterprise adoption 2025 faces persistent challenges. Regulatory uncertainty in some jurisdictions, environmental concerns around energy-intensive consensus mechanisms, and the skills gap in blockchain engineering all constrain growth.

    Integration with legacy systems remains complex. Many blockchain enterprise adoption 2025 initiatives require significant middleware development to connect blockchain networks with existing ERP, CRM, and financial systems.

    Outlook for Blockchain Enterprise Adoption 2025 and Beyond

    The momentum behind blockchain enterprise adoption 2025 suggests sustained growth. As technical limitations diminish and regulatory frameworks mature, blockchain transitions from experimental technology to standard enterprise infrastructure.

    Organizations still观望 should note that blockchain enterprise adoption 2025 leaders are building competitive advantages through reduced costs, improved transparency, and new business models. The question is shifting from whether to adopt blockchain to how quickly and strategically.

    For forward-thinking enterprises, blockchain enterprise adoption 2025 represents not just a technology upgrade but a paradigm shift in how business networks operate—more transparent, more efficient, and more trustless in the best sense of the word.

    Frequently Asked Questions About blockchain enterprise adoption 2025

    What is blockchain enterprise adoption 2025 and why is it important?

    Understanding blockchain enterprise adoption 2025 is critical for professionals and organizations navigating today’s rapidly evolving landscape. This topic directly impacts strategic decisions, operational efficiency, regulatory compliance, and long-term competitiveness in the marketplace.

    How can organizations prepare for blockchain enterprise adoption 2025?

    Organizations should conduct thorough assessments of their current capabilities, invest in team training and development, develop implementation roadmaps with clear milestones, and establish monitoring systems to track progress. Staying informed about blockchain enterprise adoption 2025 developments ensures proactive rather than reactive responses.

    What are the main challenges associated with blockchain enterprise adoption 2025?

    The primary challenges include resource constraints, skill gaps, regulatory compliance requirements, technology integration complexities, and the need for continuous adaptation. However, these challenges also present opportunities for innovation, differentiation, and competitive advantage.

    How does blockchain enterprise adoption 2025 compare to previous approaches?

    Compared to earlier methods and frameworks, blockchain enterprise adoption 2025 represents a significant evolution in both scope and impact. The pace of change has accelerated dramatically, requiring more agile, informed, and proactive approaches from all stakeholders involved.

    What should readers watch for regarding blockchain enterprise adoption 2025?

    Key indicators to monitor include regulatory developments, market adoption rates, technological breakthroughs, expert analyses, and industry best practices. Subscribing to reputable newsletters and following thought leaders provides valuable ongoing insights.

    Expert Insights and Strategic Analysis

    Industry experts and analysts have been closely monitoring developments related to blockchain enterprise adoption 2025, offering valuable perspectives on current trends and future directions that provide additional context and depth.

    Professional Perspectives

    Leading professionals emphasize that blockchain enterprise adoption 2025 represents a fundamental shift rather than an incremental change. The implications extend across organizational boundaries, affecting strategy, operations, technology infrastructure, and organizational culture simultaneously.

    Common Pitfalls to Avoid

    Several common mistakes can undermine effectiveness when addressing blockchain enterprise adoption 2025. These include underestimating implementation complexity, failing to secure adequate resources, neglecting change management, treating initiatives as one-time projects rather than ongoing programs, and insufficient stakeholder communication.

    Building a Sustainable Approach

    Sustainability in the context of blockchain enterprise adoption 2025 requires ongoing commitment, regular reassessment, and adaptive planning. Organizations should establish feedback loops, monitor key performance indicators, and adjust strategies as conditions evolve over time.

    The Competitive Advantage of Early Adoption

    Organizations that move quickly to understand and address blockchain enterprise adoption 2025 often gain significant competitive advantages including enhanced reputation, improved operational efficiency, stronger regulatory positioning, and the ability to shape industry standards and best practices.

    Recommendations for Different Organization Sizes

    The approach to blockchain enterprise adoption 2025 should vary based on organizational size. Large enterprises can invest in dedicated teams and comprehensive programs. Mid-sized organizations benefit from focused initiatives. Small organizations should prioritize foundational steps and leverage external expertise.

    Conclusion and Future Outlook

    This comprehensive analysis of blockchain enterprise adoption 2025 has explored multiple dimensions including current trends, strategic considerations, best practices, risk management, and future outlook. The key takeaway is that blockchain enterprise adoption 2025 demands proactive engagement from organizations of all sizes. By implementing the strategies and recommendations discussed, readers can position themselves effectively. Continuous learning, strategic planning, and adaptive execution remain the cornerstones of success.

    Deep Dive: Understanding blockchain enterprise adoption 2025 in Practice

    Real-World Applications and Case Studies

    Examining real-world applications of blockchain enterprise adoption 2025 reveals practical insights that theoretical frameworks alone cannot provide. Organizations across various sectors have implemented strategies addressing blockchain enterprise adoption 2025 with varying degrees of success. Their experiences offer valuable lessons for others embarking on similar journeys. Case studies demonstrate that success depends on factors including leadership commitment, resource allocation, stakeholder engagement, and adaptation to local conditions.

    Implementation Framework for blockchain enterprise adoption 2025

    A structured implementation framework for blockchain enterprise adoption 2025 typically includes several phases. The assessment phase evaluates current state and identifies gaps. The planning phase develops detailed roadmaps with timelines and resource requirements. The execution phase implements planned activities while monitoring progress. The optimization phase refines approaches based on outcomes and feedback. Each phase requires specific competencies and deliverables.

    Measuring ROI and Impact

    Demonstrating return on investment for blockchain enterprise adoption 2025 initiatives requires clear metrics and consistent measurement. Quantitative measures might include cost savings, revenue improvements, efficiency gains, and risk reduction. Qualitative indicators encompass stakeholder satisfaction, brand reputation, competitive positioning, and strategic alignment. Organizations should establish baseline measurements before implementation to enable meaningful before-and-after comparisons.

    Integration with Existing Systems

    Integrating blockchain enterprise adoption 2025 considerations into existing organizational systems and processes requires careful planning. This includes aligning with current technology infrastructure, incorporating into governance frameworks, embedding into operational procedures, and reflecting in performance metrics. Successful integration minimizes disruption while maximizing value, creating synergies rather than conflicts with established practices.

    Training and Capability Building

    Building internal capabilities for managing blockchain enterprise adoption 2025 requires comprehensive training programs. These should address both technical skills and broader competencies including strategic thinking, risk assessment, and change management. Effective programs combine formal training, hands-on experience, mentorship, and continuous learning opportunities. Investment in human capital yields the highest returns for sustainable success.

    Regulatory and Compliance Considerations

    The regulatory landscape surrounding blockchain enterprise adoption 2025 continues to evolve, with new requirements emerging regularly. Organizations must maintain awareness of applicable regulations, implement compliance measures, document their efforts, and prepare for potential audits or assessments. Engaging with regulatory bodies and industry associations provides early visibility into upcoming changes and opportunities to shape policy development.

    Final Thoughts on blockchain enterprise adoption 2025

    As this analysis demonstrates, blockchain enterprise adoption 2025 is a multifaceted topic that demands comprehensive understanding and strategic response. The organizations and individuals who invest in building knowledge, developing capabilities, and maintaining vigilance will be best positioned to thrive amid ongoing changes. The journey requires commitment, resources, and adaptability, but the potential rewards justify the investment. We encourage readers to continue exploring this topic, engaging with expert communities, and implementing the strategies discussed to achieve their objectives.
    Edge Computing and IoT Security 2025: Protecting the Distributed Computing Frontier

    0
    Edge Computing and IoT Security 2025: Protecting the Distributed Computing Frontier

    Table of Contents

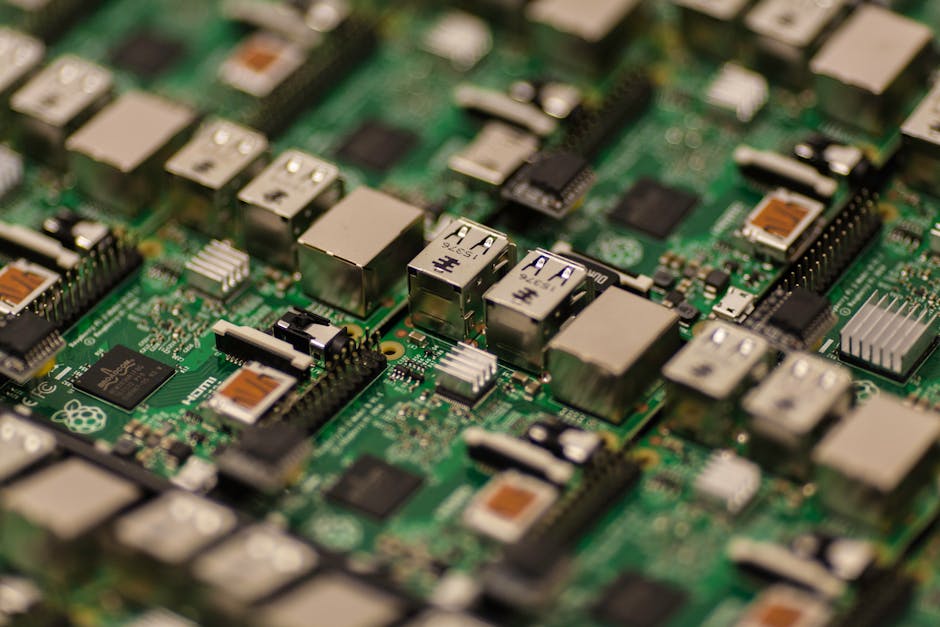
      Raspberry Pi circuit board with components and microchips representing edge computing and IoT devices Photo by Craig Dennis via Pexels
      Introduction: Edge AI and IoT Transform Computing

      Edge computing and IoT devices are experiencing explosive growth in 2025. Global IoT devices will reach 21.1 billion (14% growth), while edge AI enables real-time intelligence processing at data sources. However, this distributed architecture creates unprecedented security challenges. Key Challenge: As Forbes forecasts for 2026, “edge computing, 5G/6G deployment, and IoT devices becoming more common will witness big assaults coming from the weakest embedded device.”

      What Is Edge Computing?

      Edge computing processes data near its source rather than in centralized cloud data centers. Benefits:
      • Reduced latency for real-time applications
      • Lower bandwidth costs
      • Enhanced data privacy (local processing)
      • Continued operation during network disruptions
      Use Cases:
      • Industrial IoT and manufacturing
      • Autonomous vehicles
      • Smart cities and infrastructure
      • Healthcare devices and monitoring
      • Retail and point-of-sale systems

      Edge Computing Security Challenges

      1. Physical Security Risks

      • Edge devices often in unsecured locations
      • Physical tampering access
      • Theft of devices containing sensitive data
      • Environmental exposure damaging devices

      2. Resource Constraints

      • Limited computational power for complex security
      • Constrained memory preventing full security software
      • Battery limitations affecting always-on security
      • Cost pressures minimizing security investment

      3. Update and Patch Management

      • Distributed devices difficult to update
      • Network connectivity limitations
      • Downtime constraints in operational environments
      • Legacy devices without update mechanisms

      4. Network Security

      • Communication channel encryption
      • Authentication of edge devices to cloud
      • Man-in-the-middle attack risks
      • DDoS amplification through IoT botnets

      IoT Security: The Weakest Link

      Common IoT Vulnerabilities

      1. Default Credentials: Unchanged factory passwords
      2. Weak Authentication: No MFA, insecure protocols
      3. Unencrypted Communications: Plaintext data transmission
      4. Insecure Firmware: Vulnerabilities in device software
      5. Insufficient Logging: Unable to detect compromises

      Notable IoT Security Incidents

      • Mirai botnet precedent: millions of IoT devices weaponized
      • Smart home device compromises enabling surveillance
      • Industrial IoT attacks disrupting manufacturing
      • Medical IoT vulnerabilities risking patient safety

      Edge AI Security Considerations

      Edge AI brings intelligence to devices, but also risks:

      1. Model Security

      • AI model theft from edge devices
      • Adversarial attacks manipulating edge AI decisions
      • Model poisoning during edge training
      • Intellectual property protection

      2. Data Privacy at the Edge

      • Sensitive data processed locally requires protection
      • Federated learning privacy implications
      • Data residency and sovereignty compliance

      Best Practices for Edge and IoT Security

      Device Security

      1. Hardware root of trust and secure boot
      2. Strong default credentials (unique per device)
      3. Encrypted storage for sensitive data
      4. Tamper detection and response
      5. Secure firmware update mechanisms

      Network Security

      1. TLS/DTLS for all communications
      2. Certificate-based device authentication
      3. Network segmentation isolating IoT
      4. Anomaly detection for device behavior

      Lifecycle Management

      1. Device inventory and asset tracking
      2. Regular vulnerability scanning
      3. Automated patch deployment
      4. End-of-life device decommissioning

      Conclusion: Securing the Distributed Future

      Edge computing and IoT enable transformative applications but create distributed security challenges. Organizations must implement security from device design through deployment and lifecycle management. Success requires: Hardware security, encrypted communications, continuous monitoring, and lifecycle management.
      Sources: IoT Evolution World, Sealevel Systems, Semi Engineering, RTInsights, IoT Analytics
      edge computing IoT security 2025 - overview of edge computing IoT security 2025 concepts and framework
      edge computing IoT security 2025 - edge computing IoT security 2025 implementation and architecture diagram
      edge computing IoT security 2025 - edge computing IoT security 2025 statistics and key metrics visualization

      The Rise of Edge Computing IoT Security 2025 Challenges

      Edge computing IoT security 2025 emerged as one of the most critical challenges facing modern enterprises. With billions of connected devices deployed across industrial, commercial, and consumer environments, protecting distributed infrastructure required fundamentally new approaches. Traditional security models designed for centralized data centers simply could not scale to address this rapidly expanding attack surface.

      The convergence of edge processing and connected devices amplified risks dramatically. Devices operating far from centralized data centers often lacked physical security controls, reliable network connections, and dedicated monitoring. Security teams had to address these fundamental limitations while defending against increasingly sophisticated attack techniques that evolved faster than defensive capabilities.

      Organizations deploying distributed infrastructure discovered that challenges multiplied with each additional device. Management overhead exceeded traditional security operations capacity. This scale challenge drove innovation in automated security tools and architectural approaches specifically designed for distributed environments where manual intervention was impractical or impossible.

      The financial stakes of inadequate protection grew substantially. Organizations deploying thousands of connected devices faced potential liability from compromised systems causing physical damage, data breaches, or service disruption. Insurance providers began requiring evidence of protective controls before issuing policies covering IoT-enabled operations and distributed infrastructure deployments.

      Why Edge Computing IoT Security 2025 Matters Now

      The urgency of distributed infrastructure security stems from rapid deployment growth across every industry. Organizations installed smart sensors, connected cameras, industrial controllers, and environmental monitors at unprecedented rates. Each new device potentially introduced vulnerabilities, and the challenge multiplied with every addition to networks that were already difficult to monitor.

      Attackers recognized edge devices as soft targets, making this a pressing concern for security teams. Many connected devices shipped with default credentials, unpatched firmware, and minimal built-in security features. Teams had to contend with an enormous attack surface of inherently vulnerable devices that could not easily be hardened through software updates alone.

      Regulatory requirements also drove priorities in this area. Data protection regulations extended to data collected at edge locations, creating compliance obligations for organizations that had previously treated edge data as outside regulatory scope. Demonstrable security controls across distributed environments became a legal requirement rather than merely a best practice.

      The convergence of operational technology and IT created additional urgency. Industrial control systems that had operated in isolation for decades now connected to corporate networks and cloud platforms. This connectivity introduced IT security threats to environments where failures could cause physical harm, raising the stakes significantly beyond data loss or system downtime.

      Threat Landscape for Distributed Environments

      The threat landscape for distributed infrastructure security included diverse and evolving attack vectors. Botnet recruitment of compromised devices remained prevalent as attackers harvested vulnerable endpoints for distributed denial of service campaigns. Successors to the infamous Mirai botnet launched attacks exceeding several terabits per second, overwhelming traditional mitigation capabilities and causing widespread service disruption.

      Supply chain attacks targeting device firmware complicated defense efforts significantly. Malicious firmware updates could compromise thousands of devices simultaneously before detection. Security teams required verification of firmware integrity throughout device lifecycles, from manufacturing through deployment to decommissioning, creating complex provenance tracking requirements.

      Ransomware targeting industrial control systems emerged as a particularly dangerous threat. When attackers compromised edge devices controlling physical processes, they could demand ransom under threat of operational disruption or safety incidents. These attacks blurred the line between cybercrime and physical extortion, creating new categories of risk for organizations managing distributed infrastructure.

      Protocol-level attacks against industrial communication systems proved particularly challenging. Attackers exploited vulnerabilities in Modbus, DNP3, and other industrial protocols that lacked built-in security features. Securing these protocols required network-level controls since the protocols themselves could not be easily modified without breaking compatibility with existing equipment.

      Industrial IoT Introduces Unique Risks

      Industrial IoT introduced unique challenges for edge computing IoT security 2025. Manufacturing facilities deployed sensors controlling physical processes where security failures caused real-world damage. Safety-critical reliability requirements meant that security measures could not introduce operational risks through false positives or system interruptions that could halt production or endanger worker safety.

      Legacy industrial equipment complicated implementation significantly. Many machines lacked modern security capabilities and could not easily be upgraded with current security software. Strategies had to accommodate devices running outdated operating systems that vendors no longer supported, creating extended vulnerability windows that attackers could exploit through known unpatched vulnerabilities.

      The convergence of operational technology and IT networks created new concerns. Previously isolated industrial networks now connected to corporate systems for data analytics and remote management. Bridging these environments required security approaches that protected both network domains without compromising operational availability or introducing latency into control systems that required real-time response.

      Personnel training represented another significant challenge. Industrial operations staff often lacked cybersecurity expertise, while IT security teams lacked understanding of operational technology requirements. Effective defense required cross-training and collaboration between these traditionally separate organizational functions, which often had different reporting structures and priorities.

      Supply chain complexity in industrial environments created additional exposure. Industrial devices often passed through multiple vendors and integrators before deployment. Each handoff represented a potential security compromise point. Organizations responded with stricter vendor requirements and device authentication protocols, though implementation remained inconsistent across the industrial sector.

      Architectural Approaches to Distributed Defense

      Security architecture for distributed environments evolved significantly from traditional models. Distributed security controls replaced centralized firewalls as primary defense mechanisms. Security had to exist at every node rather than relying on perimeter protection that became meaningless when thousands of devices operated beyond traditional network boundaries.

      Zero trust principles adapted for edge environments formed the backbone of modern defense strategies. Every device, connection, and data flow required verification regardless of network location. Implementing zero trust at device scale posed unique challenges, particularly for resource-constrained devices that could not run sophisticated authentication agents or encryption protocols.

      Software-defined networking enabled dynamic security policy enforcement across distributed environments. Security policies adjusted automatically based on device behavior, threat intelligence, and business context. This adaptability proved essential for environments where device populations changed frequently and threat conditions evolved rapidly throughout the deployment lifecycle.

      Security gateways became essential architectural components for edge deployments. These purpose-built devices provided firewall, intrusion detection, and encryption capabilities for groups of connected devices that individually lacked sufficient processing power for comprehensive security controls. Gateway-based architectures balanced protection with resource constraints effectively.

      Microsegmentation and Network Isolation

      Microsegmentation proved essential for limiting breach impact. By isolating device groups, organizations contained compromised devices from threatening broader networks. When a single sensor was compromised, microsegmentation prevented lateral movement to other devices and critical systems. This containment strategy significantly reduced average breach severity for well-implemented deployments.

      Network slicing in 5G environments enhanced isolation capabilities within security frameworks. Dedicated network paths for IoT traffic reduced interception risks and provided guaranteed bandwidth for critical communications. The combination of 5G slicing and microsegmentation created layered isolation that proved highly effective for large-scale deployments spanning geographic distances.

      Implementation challenges included managing segmentation rules across thousands of device groups while maintaining operational flexibility. Automated policy generation tools emerged to address this complexity, using machine learning to suggest optimal segmentation strategies based on device behavior patterns and risk profiles that changed over time.

      Cloud-based security management platforms enabled centralized policy administration across distributed microsegmented environments. These platforms provided single-pane-of-glass visibility into security posture across all locations while pushing policy updates automatically. The cloud management approach solved scaling challenges that traditional on-premises security management tools could not handle.

      Edge Computing IoT Security 2025 Device-Level Measures

      Device-level security represented the foundation of effective defense. Secure boot processes ensured devices ran only verified firmware, preventing attackers from replacing operating systems with malicious alternatives. Hardware roots of trust in every connected device provided cryptographic verification that software-only solutions could not match or replicate.

      Hardware security modules gained prominence as organizations recognized the limitations of software-based key protection. These dedicated security chips provided cryptographic operations and key storage that resisted tampering even when devices were physically compromised. Hardware-based protection proved essential for devices deployed in accessible locations.

      End-to-end encryption became standard practice for data transmitted between edge devices and central systems. Lightweight encryption protocols developed specifically for resource-constrained devices addressed power and processing limitations that made standard encryption impractical for many battery-powered or low-cost connected devices.

      Device identity management proved foundational to all other security measures. Each device required a unique cryptographic identity that could not be spoofed or stolen. Certificate-based identity systems scaled better than shared secrets, though managing certificate lifecycles across millions of devices required robust automated infrastructure.

      AI-Driven Security Solutions

      Artificial intelligence transformed defense approaches significantly. AI-powered anomaly detection identified compromised devices through behavioral analysis that recognized deviations from normal operation patterns. These solutions detected threats that signature-based systems missed entirely, including novel attacks and slow-moving compromises that unfolded over weeks.

      Federated learning enabled collaborative threat intelligence across device populations. Devices shared threat indicators without exposing raw data, preserving privacy while improving detection capabilities. This collaborative approach proved particularly valuable for large deployments where centralized analysis of all device data was impractical due to bandwidth or regulatory constraints.

      Autonomous response capabilities enhanced defense significantly within security programs. When threats were detected, compromised devices could be automatically quarantined from the network, reducing incident response time from hours to seconds. However, autonomous response required careful tuning to avoid false positives that could disrupt critical operations in industrial environments where downtime carried significant costs.

      Predictive analytics represented the frontier of defense capabilities. AI models anticipated attacks before they occurred based on threat pattern analysis and environmental indicators. This shift from reactive to proactive defense marked a significant maturation in how organizations protected distributed infrastructure against emerging threats that had not yet been observed in their specific environments.

      Governance, Compliance, and Future Readiness

      Governance frameworks adapted to distributed environment requirements. Organizations established policies for device lifecycle management from procurement through decommissioning, ensuring security controls applied at every stage. Comprehensive governance addressed not only technical controls but also vendor selection criteria and device disposal procedures that prevented data recovery from decommissioned equipment.

      Compliance challenges multiplied as data collected at edge locations crossed multiple jurisdictions with different regulatory requirements. Understanding where data originated, was processed, and was stored became essential for maintaining compliance. Automated data governance tools emerged to help organizations track data flows across complex distributed environments spanning international boundaries.

      Building future-ready programs requires continuous assessment of device security posture rather than point-in-time audits. Investment in specialized talent with both IoT and distributed systems expertise remains essential, as these skills are scarce in traditional security teams. The landscape will continue evolving as device counts grow and attack sophistication increases.

      Organizations that prioritize distributed infrastructure protection will build resilient distributed infrastructure capable of supporting digital transformation initiatives safely. Those that treat distributed security as an afterthought will face escalating risks as attackers continue targeting the expanding attack surface that connected devices create across every industry sector and operational environment.

      The regulatory landscape will likely continue evolving alongside security developments. New standards for device security are emerging from industry consortia and government agencies. Organizations should anticipate mandatory security requirements for connected devices and prepare compliance programs that can adapt to evolving standards across multiple jurisdictions simultaneously.

      Emerging Standards and Industry Collaboration

      Industry standards organizations accelerated development of security frameworks specifically for distributed infrastructure. The Internet Engineering Task Force and National Institute of Standards and Technology released guidelines for edge device security that provided implementation benchmarks for organizations struggling with practical deployment challenges.

      Industry consortia emerged to address shared challenges. Manufacturing companies formed alliances to establish security requirements for industrial IoT vendors, leveraging collective purchasing power to demand better security practices from equipment suppliers. These collaborative approaches proved more effective than individual company initiatives at driving vendor security improvements.

      Certification programs for edge devices gained traction. Independent testing laboratories began offering security certifications that verified devices met baseline security requirements including secure boot, encryption support, and vulnerability disclosure practices. Government procurement agencies began requiring these certifications for connected device purchases, creating market incentives for improved security.

      The convergence of physical and digital security became a priority for organizations managing distributed infrastructure. Physical security measures including tamper-resistant enclosures, secure installation practices, and environmental monitoring complemented digital security controls. Organizations recognized that edge devices in physically accessible locations required protection against both cyber and physical attacks simultaneously.

      International cooperation on threat intelligence improved through structured information sharing frameworks. Organizations across borders shared indicators of compromise, attack patterns, and vulnerability information through automated platforms. This collaboration proved particularly valuable for multinational organizations managing distributed infrastructure across multiple regulatory jurisdictions with different requirements.

      5G Network Security in 2025: Vulnerabilities, Threats, and Protection Strategies for Next-Gen Connectivity

      0
      5G Network Security in 2025: Vulnerabilities, Threats, and Protection Strategies for Next-Gen Connectivity

      Table of Contents

        Modern 5G cell tower with technology components against blue sky representing next-generation network infrastructure

        Photo by Ulrick Trappschuh via Pexels

        Introduction: 5G Security Challenges and Opportunities

        As 5G networks expand globally, security concerns intensify. The 5G security market reached $3.63 billion in 2024, projected to grow at 40% CAGR through 2030, reflecting both opportunity and urgency in securing next-generation connectivity. Singapore’s CIDeX 2025 featured exercises involving attacks on 5G networks and power grid disruptions, while Ericsson and Deutsche Telekom conducted collaborative BugBash testing to proactively reinforce private 5G network security.

        5G Security Architecture

        Enhanced Security Features vs. New Vulnerabilities

        Security Improvements Over 4G:
        • Enhanced encryption algorithms
        • Improved authentication mechanisms
        • Network slicing isolation
        • Software-defined security
        New Attack Vectors:
        • Expanded attack surface from massive IoT device connectivity
        • Virtualized network functions introducing software vulnerabilities
        • Edge computing bringing computation closer to users (and attackers)
        • Supply chain complexity with multi-vendor environments

        Key 5G Security Vulnerabilities

        1. Authentication and Encryption Weaknesses

        • IMSI catchers and false base stations
        • Downgrade attacks forcing less secure protocols
        • Subscriber identity privacy issues

        2. Network Slicing Security

        • Slice isolation failures enabling cross-slice attacks
        • Resource exhaustion in shared infrastructure
        • Slice orchestration vulnerabilities

        3. API Security Risks

        • Open APIs for network function exposure
        • Authentication and authorization flaws
        • API abuse and DDoS attacks

        4. Supply Chain Risks

        • Equipment from potentially compromised vendors
        • Firmware and software updates as attack vectors
        • Hardware backdoors and implants

        5G and IoT: Massive Attack Surface

        The Scale: IoT devices expected to reach 21.1 billion in 2025 (14% growth), with many connecting via 5G. Security Challenges:
        • Resource-constrained devices with limited security
        • Firmware update mechanisms often insecure
        • Default credentials and weak authentication
        • Lack of security standards enforcement
        Attack Scenarios:
        • IoT botnets leveraging 5G bandwidth
        • DDoS attacks at unprecedented scale
        • Critical infrastructure targeting through IoT
        • Privacy violations from ubiquitous sensing

        5G Security Best Practices

        For Network Operators

        1. Implement Zero Trust architecture
        2. Network slicing security with strong isolation
        3. Continuous security monitoring and threat intelligence
        4. Vendor security assessments and supply chain security
        5. Regular penetration testing and vulnerability assessments

        For Enterprise 5G Users

        1. Private 5G network security hardening
        2. IoT device security and inventory
        3. Network segmentation and access control
        4. Encryption for sensitive data over 5G
        5. Incident response plans for 5G-specific threats

        Regulatory Landscape for 5G Security

        Government Actions:
        • Restrictions on Huawei and ZTE equipment in many countries
        • Security certification requirements for 5G equipment
        • Open RAN adoption for supply chain diversification
        • National security reviews of 5G deployments

        Conclusion: Securing the 5G Future

        5G networks promise transformative connectivity but introduce significant security challenges. As deployment accelerates and IoT devices proliferate, securing 5G infrastructure becomes critical for business operations, critical infrastructure, and national security. Key Actions:
        • Implement comprehensive 5G security architecture
        • Address IoT security from device design through deployment
        • Continuous monitoring and threat intelligence
        • Supply chain security and vendor management

        Sources: Industrial Cyber, Ericsson, LinkedIn market analysis, Forbes, IoT Analytics

        5G network security 2025 - overview of 5G network security 2025 concepts and framework
        5G network security 2025 - 5G network security 2025 implementation and architecture diagram
        5G network security 2025 - 5G network security 2025 statistics and key metrics visualization

        Understanding 5G Network Security 2025 Challenges

        As fifth-generation networks reach global maturity, 5G network security 2025 has emerged as one of the most critical infrastructure protection challenges. The expanded attack surface, denser infrastructure, and new architectural paradigms create vulnerabilities that previous generations never faced.

        With over 2.5 billion 5G connections worldwide by 2025, the stakes for 5G network security 2025 could not be higher. Everything from autonomous vehicles to remote surgery depends on the integrity and availability of these networks.

        Architecture Vulnerabilities in 5G Network Security 2025

        Software-Defined Networks

        Unlike 4G’s hardware-centric architecture, 5G relies heavily on software-defined networking and network function virtualization. This shift expands the 5G network security 2025 attack surface from physical infrastructure to software layers accessible through APIs and orchestration platforms.

        SDN controllers, which manage traffic routing decisions, represent high-value targets. A compromise here could redirect traffic, cause service disruptions, or enable eavesdropping. 5G network security 2025 frameworks must protect these controllers with particular rigor.

        Network slicing, a key 5G feature, introduces isolation challenges. While slices are logically separated, shared underlying infrastructure means vulnerabilities can potentially cross slice boundaries. 5G network security 2025 researchers have demonstrated side-channel attacks exploiting this shared resource model.

        Edge Computing Risks

        5G pushes computing to the network edge, reducing latency but distributing infrastructure across thousands of locations. 5G network security 2025 must address physical security at edge sites that lack the hardened environments of centralized data centers.

        Multi-access edge computing platforms process sensitive data closer to users, creating new data residency and privacy concerns. The 5G network security 2025 paradigm requires encryption at rest and in transit across distributed edge nodes, with secure key management.

        Major Threat Vectors in 5G Network Security 2025

        Rogue Base Stations and IMSI Catchers

        While 5G introduced improved authentication protocols, 5G network security 2025 researchers documented evolved rogue base station attacks. These fake cell towers exploit protocol weaknesses to intercept traffic, track users, or launch denial-of-service attacks.

        Stingray-type devices have been modernized for 5G, with commercial-grade equipment available. Addressing these threats, 5G network security 2025 strategies include mutual authentication enhancements and network monitoring for anomalous base station behavior.

        Supply Chain Risks

        Equipment supply chains remain a central concern in 5G network security 2025. The debate over vendor trustworthiness, particularly regarding Chinese manufacturers, led many countries to restrict or ban certain suppliers. However, supply chain security extends beyond geopolitics.

        Firmware integrity, component authentication, and hardware trojan detection are all active areas within 5G network security 2025. Zero-trust supply chain frameworks, where every component is verified regardless of origin, are gaining adoption among security-conscious operators.

        IoT and Connected Device Vulnerabilities

        5G’s promise of massive IoT connectivity means billions of devices access the network. 5G network security 2025 must contend with devices that often lack adequate security controls, from smart meters to industrial sensors.

        Botnets leveraging compromised 5G-connected IoT devices could launch unprecedented attacks. The 5G network security 2025 framework requires network-level protections including device onboarding verification, anomaly detection, and automated quarantine of compromised devices.

        Protection Strategies for 5G Network Security 2025

        Zero Trust Architecture

        Implementing zero trust principles is fundamental to 5G network security 2025. Rather than trusting devices within the network perimeter, every access request is verified, authenticated, and authorized regardless of origin.

        For 5G operators, this means micro-segmentation of network functions, continuous authentication of connected devices, and real-time policy enforcement. 5G network security 2025 zero trust implementations leverage AI-driven behavioral analysis to detect anomalies.

        Encryption and Key Management

        5G introduced stronger encryption standards than 4G, but 5G network security 2025 requires going beyond defaults. End-to-end encryption for sensitive communications, quantum-resistant algorithms for long-term protection, and robust key rotation protocols are essential.

        Subscriber identity protection improved with 5G’s Subscription Permanent Identifier encryption, but 5G network security 2025 researchers identified implementation flaws in some deployments. Continuous auditing of cryptographic implementations is necessary.

        AI-Powered Threat Detection

        The scale and complexity of 5G networks make manual monitoring impossible. 5G network security 2025 relies on AI and machine learning for real-time threat detection, anomaly identification, and automated response.

        Machine learning models trained on network traffic patterns can identify deviations indicating attacks. These 5G network security 2025 systems must balance sensitivity to avoid false positives while catching genuine threats before damage occurs.

        Regulatory Landscape for 5G Network Security 2025

        Government Mandates

        Governments worldwide established 5G network security 2025 requirements. The EU’s 5G Toolbox provides a coordinated framework, while the US uses executive orders and FCC regulations. These mandates cover vendor restrictions, security baselines, and incident reporting.

        Critical infrastructure designations for 5G networks in many countries trigger additional 5G network security 2025 obligations, including stricter incident reporting, mandatory risk assessments, and government oversight of security practices.

        Industry Standards

        3GPP, GSMA, and NIST all contributed standards for 5G network security 2025. The 3GPP Release 17 and 18 specifications enhanced security protocols, while NIST’s 5G cybersecurity guidelines provide implementation frameworks for operators.

        Security assurance specifications within 3GPP enable standardized testing of network equipment. This 5G network security 2025 standardization helps operators verify vendor claims and identify implementation weaknesses.

        Future Outlook on 5G Network Security 2025

        As 5G networks continue evolving toward 5G Advanced and eventually 6G, 5G network security 2025 investments lay critical groundwork. The integration of AI-native security, quantum-safe cryptography, and enhanced privacy protections will shape the next generation.

        Private 5G networks deployed by enterprises represent a growing segment requiring tailored 5G network security 2025 approaches. These deployments often lack the security resources of major operators but face similar threats.

        The convergence of 5G with satellite networks introduces another dimension. Non-terrestrial network integration expands coverage but creates new 5G network security 2025 challenges around satellite link security, ground station vulnerabilities, and cross-network authentication.

        Ultimately, 5G network security 2025 is not a destination but a continuous process. Threat actors evolve alongside technology, meaning security frameworks must remain adaptive. Organizations that treat 5G security as an ongoing program rather than a one-time implementation will be best positioned to protect their networks, users, and data in an increasingly connected world.

        Frequently Asked Questions About 5G network security 2025

        What is 5G network security 2025 and why is it important?

        Understanding 5G network security 2025 is critical for professionals and organizations navigating today’s rapidly evolving landscape. This topic directly impacts strategic decisions, operational efficiency, regulatory compliance, and long-term competitiveness in the marketplace.

        How can organizations prepare for 5G network security 2025?

        Organizations should conduct thorough assessments of their current capabilities, invest in team training and development, develop implementation roadmaps with clear milestones, and establish monitoring systems to track progress. Staying informed about 5G network security 2025 developments ensures proactive rather than reactive responses.

        What are the main challenges associated with 5G network security 2025?

        The primary challenges include resource constraints, skill gaps, regulatory compliance requirements, technology integration complexities, and the need for continuous adaptation. However, these challenges also present opportunities for innovation, differentiation, and competitive advantage.

        How does 5G network security 2025 compare to previous approaches?

        Compared to earlier methods and frameworks, 5G network security 2025 represents a significant evolution in both scope and impact. The pace of change has accelerated dramatically, requiring more agile, informed, and proactive approaches from all stakeholders involved.

        What should readers watch for regarding 5G network security 2025?

        Key indicators to monitor include regulatory developments, market adoption rates, technological breakthroughs, expert analyses, and industry best practices. Subscribing to reputable newsletters and following thought leaders provides valuable ongoing insights.

        Expert Insights and Strategic Analysis

        Industry experts and analysts have been closely monitoring developments related to 5G network security 2025, offering valuable perspectives on current trends and future directions that provide additional context and depth.

        Professional Perspectives

        Leading professionals emphasize that 5G network security 2025 represents a fundamental shift rather than an incremental change. The implications extend across organizational boundaries, affecting strategy, operations, technology infrastructure, and organizational culture simultaneously.

        Common Pitfalls to Avoid

        Several common mistakes can undermine effectiveness when addressing 5G network security 2025. These include underestimating implementation complexity, failing to secure adequate resources, neglecting change management, treating initiatives as one-time projects rather than ongoing programs, and insufficient stakeholder communication.

        Building a Sustainable Approach

        Sustainability in the context of 5G network security 2025 requires ongoing commitment, regular reassessment, and adaptive planning. Organizations should establish feedback loops, monitor key performance indicators, and adjust strategies as conditions evolve over time.

        The Competitive Advantage of Early Adoption

        Organizations that move quickly to understand and address 5G network security 2025 often gain significant competitive advantages including enhanced reputation, improved operational efficiency, stronger regulatory positioning, and the ability to shape industry standards and best practices.

        Recommendations for Different Organization Sizes

        The approach to 5G network security 2025 should vary based on organizational size. Large enterprises can invest in dedicated teams and comprehensive programs. Mid-sized organizations benefit from focused initiatives. Small organizations should prioritize foundational steps and leverage external expertise.

        Conclusion and Future Outlook

        This comprehensive analysis of 5G network security 2025 has explored multiple dimensions including current trends, strategic considerations, best practices, risk management, and future outlook. The key takeaway is that 5G network security 2025 demands proactive engagement from organizations of all sizes. By implementing the strategies and recommendations discussed, readers can position themselves effectively. Continuous learning, strategic planning, and adaptive execution remain the cornerstones of success.

        Deep Dive: Understanding 5G network security 2025 in Practice

        Real-World Applications and Case Studies

        Examining real-world applications of 5G network security 2025 reveals practical insights that theoretical frameworks alone cannot provide. Organizations across various sectors have implemented strategies addressing 5G network security 2025 with varying degrees of success. Their experiences offer valuable lessons for others embarking on similar journeys. Case studies demonstrate that success depends on factors including leadership commitment, resource allocation, stakeholder engagement, and adaptation to local conditions.

        Implementation Framework for 5G network security 2025

        A structured implementation framework for 5G network security 2025 typically includes several phases. The assessment phase evaluates current state and identifies gaps. The planning phase develops detailed roadmaps with timelines and resource requirements. The execution phase implements planned activities while monitoring progress. The optimization phase refines approaches based on outcomes and feedback. Each phase requires specific competencies and deliverables.

        Measuring ROI and Impact

        Demonstrating return on investment for 5G network security 2025 initiatives requires clear metrics and consistent measurement. Quantitative measures might include cost savings, revenue improvements, efficiency gains, and risk reduction. Qualitative indicators encompass stakeholder satisfaction, brand reputation, competitive positioning, and strategic alignment. Organizations should establish baseline measurements before implementation to enable meaningful before-and-after comparisons.

        Integration with Existing Systems

        Integrating 5G network security 2025 considerations into existing organizational systems and processes requires careful planning. This includes aligning with current technology infrastructure, incorporating into governance frameworks, embedding into operational procedures, and reflecting in performance metrics. Successful integration minimizes disruption while maximizing value, creating synergies rather than conflicts with established practices.

        Training and Capability Building

        Building internal capabilities for managing 5G network security 2025 requires comprehensive training programs. These should address both technical skills and broader competencies including strategic thinking, risk assessment, and change management. Effective programs combine formal training, hands-on experience, mentorship, and continuous learning opportunities. Investment in human capital yields the highest returns for sustainable success.

        Regulatory and Compliance Considerations

        The regulatory landscape surrounding 5G network security 2025 continues to evolve, with new requirements emerging regularly. Organizations must maintain awareness of applicable regulations, implement compliance measures, document their efforts, and prepare for potential audits or assessments. Engaging with regulatory bodies and industry associations provides early visibility into upcoming changes and opportunities to shape policy development.

        Final Thoughts on 5G network security 2025

        As this analysis demonstrates, 5G network security 2025 is a multifaceted topic that demands comprehensive understanding and strategic response. The organizations and individuals who invest in building knowledge, developing capabilities, and maintaining vigilance will be best positioned to thrive amid ongoing changes. The journey requires commitment, resources, and adaptability, but the potential rewards justify the investment. We encourage readers to continue exploring this topic, engaging with expert communities, and implementing the strategies discussed to achieve their objectives.

        Additional Resources and Next Steps for 5G network security 2025

        For readers looking to deepen their understanding of 5G network security 2025, numerous resources are available. Professional certifications offer structured learning paths, while industry conferences provide opportunities for networking and knowledge sharing. Online communities and forums enable peer discussions and problem-solving. Academic research papers and industry reports deliver in-depth analysis for advanced practitioners.

        Recommended Reading on 5G network security 2025

        Several authoritative publications regularly cover 5G network security 2025 developments. Subscribing to these sources ensures ongoing awareness of trends, breakthroughs, and best practices. Books by recognized experts provide comprehensive frameworks, while academic journals offer peer-reviewed research findings that validate practical approaches.

        Taking Action on 5G network security 2025

        The most effective next step is to assess your organization’s current position relative to 5G network security 2025 and identify priority areas for improvement. Starting with a focused pilot project allows for learning and refinement before broader rollout. Documenting lessons learned and sharing successes builds momentum and organizational support for larger initiatives.

        Stay informed about 5G network security 2025 by following informbytes.com for regular updates, analysis, and expert commentary on this evolving topic.

        Data Privacy Regulations 2025: GDPR Evolution, Global Compliance, and Emerging Privacy Laws

        0
        Data Privacy Regulations 2025: GDPR Evolution, Global Compliance, and Emerging Privacy Laws

        Table of Contents

          Surveillance cameras on wall representing data privacy and security protection

          Photo by Scott Webb via Pexels

          Introduction: The Expanding Global Privacy Regulatory Landscape

          As 2025 progresses, data privacy regulations evolve globally. The EU’s GDPR faces proposed reforms, the UK’s Data Use and Access Act 2025 diverges from EU standards, India strengthens privacy protections with new rules effective November 2025.

          GDPR in 2025: Evolution and Reform

          Proposed Simplifications:
          • Reduced administrative burden for SMEs
          • Streamlined documentation
          • Clearer guidance and definitions
          Enforcement Trends: Rising fines, focus on repeat violations, cross-border cooperation improving.

          India’s New Privacy Rules (Nov 2025)

          Requires Meta, Google, OpenAI to:
          • Minimize personal data collection
          • Provide user control over data
          • Enhanced consent requirements

          US State Privacy Laws Expanding

          States with active laws: California, Virginia, Colorado, Connecticut, Utah, Iowa, Montana, Oregon, Texas, Delaware, plus more effective 2026-2027. Challenge: No federal law creates compliance patchwork.

          Best Practices

          1. Privacy by design and default
          2. Consent Management Platforms
          3. Data subject rights automation
          4. Vendor privacy management
          5. Privacy-enhancing technologies (PETs)

          Conclusion

          Organizations must implement robust privacy programs spanning jurisdictions, adopt privacy-by-design, and treat privacy as competitive advantage.

          Sources: TechPolicy.Press, Reuters, BDO, The Guardian

          data privacy regulations 2025 - overview of data privacy regulations 2025 concepts and framework
          data privacy regulations 2025 - data privacy regulations 2025 implementation and architecture diagram
          data privacy regulations 2025 - data privacy regulations 2025 statistics and key metrics visualization

          How Data Privacy Regulations 2025 Are Reshaping Global Business

          The landscape of data privacy regulations 2025 has transformed dramatically from just a few years ago. What began with GDPR as a European initiative has now proliferated into a complex web of laws spanning every major economy. Organizations that once treated privacy as an afterthought now find it central to their operational strategy.

          In 2025 alone, more than 40 new or amended privacy laws took effect worldwide. The data privacy regulations 2025 framework represents the most sweeping legal shift since the internet’s commercialization. Companies face overlapping jurisdictions, conflicting requirements, and penalties that can reach billions.

          Key Changes in Data Privacy Regulations 2025

          GDPR Evolution Under Data Privacy Regulations 2025

          The General Data Protection Regulation continues to serve as the template for data privacy regulations 2025, but it has evolved significantly. The European Commission introduced amendments clarifying automated decision-making boundaries, strengthening consent mechanisms for minors, and expanding data subject rights around AI-processed information.

          Enforcement has also intensified. Under data privacy regulations 2025, GDPR fines exceeded 2.8 billion euros collectively, with Meta and Amazon facing the largest penalties. Regulators now coordinate cross-border investigations more efficiently through the European Data Protection Board’s reinforced framework.

          New guidance on cookie consent represents another major shift. The data privacy regulations 2025 updates effectively ban dark patterns and require genuine choice architecture. Pop-up consent banners must offer equivalent visibility for accept and reject options, a change that forced thousands of websites to redesign their UX.

          United States Privacy Laws in Data Privacy Regulations 2025

          The American approach to data privacy regulations 2025 remains fragmented but is coalescing. Following California’s CCPA/CPRA, fifteen states enacted comprehensive privacy laws by mid-2025, including Texas, Florida, Oregon, and Montana. Each statute carries unique definitions and exemptions.

          The American Privacy Rights Act, proposed federally, gained significant momentum in 2025. If passed, it would establish a national baseline preempting certain state provisions. However, data privacy regulations 2025 experts note that state laws with stricter requirements would likely survive, creating a hybrid compliance environment.

          Sectoral rules also expanded. The FTC’s updated Health Breach Notification Rule and new children’s privacy rules under COPPA 2.0 added layers to data privacy regulations 2025 in the US, particularly affecting health apps and educational technology platforms.

          Emerging Global Privacy Laws Under Data Privacy Regulations 2025

          Asia-Pacific Developments

          Asia-Pacific nations accelerated their privacy frameworks significantly. India’s Digital Personal Data Protection Act, operationalized in 2025, brings 1.4 billion people under formal privacy protection. The law introduces consent managers, data fiduciary obligations, and cross-border transfer restrictions.

          China’s Personal Information Protection Law continued to evolve within data privacy regulations 2025, with new rules on data exports requiring security assessments. Japan, South Korea, and Singapore all updated their statutes to address AI processing and biometric data.

          Australia’s Privacy Act review concluded with amendments expanding the definition of personal information and introducing a statutory tort for serious invasions of privacy, aligning with broader data privacy regulations 2025 trends.

          Latin America and Africa

          Brazil’s LGPD enforcement matured under data privacy regulations 2025, with ANPD issuing its first major fines. Mexico, Argentina, and Colombia advanced their own frameworks. In Africa, Nigeria’s NDPA and South Africa’s POPIA enforcement expanded, while Kenya and Rwanda introduced new bills.

          The global south’s engagement with data privacy regulations 2025 reflects growing awareness that data sovereignty and digital rights are development priorities, not just compliance checkboxes.

          AI and Data Privacy Regulations 2025

          Artificial intelligence is the defining challenge for data privacy regulations 2025. Regulators worldwide grappled with how existing privacy frameworks apply to AI training, inference, and automated outputs. The EU AI Act, working in tandem with GDPR, created the most comprehensive approach.

          Key issues include training data provenance, the right to object to profiling, and transparency obligations for AI-generated decisions. Data privacy regulations 2025 increasingly require organizations to conduct Data Protection Impact Assessments specifically for AI systems.

          The concept of privacy by design has been extended to AI by design under data privacy regulations 2025. This means embedding privacy safeguards into model architecture, data pipelines, and deployment infrastructure from the earliest stages.

          Cross-Border Data Transfers Under Data Privacy Regulations 2025

          International data flows remain one of the most complex aspects of data privacy regulations 2025. The EU’s new Data Privacy Framework replaced SCCs for US transfers, but legal challenges persist. Other countries adopted similar adequacy-based approaches.

          Binding Corporate Rules remain viable for multinational organizations, but approval timelines stretch months. Under data privacy regulations 2025, transfer impact assessments must account for surveillance risks in destination countries, adding analytical burden.

          Data localization mandates expanded in several jurisdictions. Russia, China, India, and Indonesia all tightened requirements keeping certain data within national borders, complicating cloud architecture strategies under data privacy regulations 2025.

          Compliance Strategies for Data Privacy Regulations 2025

          Building a Privacy Program

          Organizations navigating data privacy regulations 2025 need structured privacy programs. Key elements include data mapping and inventory, privacy policies aligned to applicable jurisdictions, vendor risk management, and incident response protocols.

          Privacy-enhancing technologies have become essential. Tools for data minimization, pseudonymization, and differential privacy help organizations meet data privacy regulations 2025 requirements while maintaining analytical capabilities. Investment in PETs grew 45% year-over-year.

          Training and awareness remain critical. Data privacy regulations 2025 expect organizations to demonstrate a culture of privacy, not just technical compliance. Regular workforce training, documented accountability, and privacy by design processes are baseline expectations.

          Technology Solutions

          Privacy management platforms have matured significantly. Leading tools now offer automated data discovery, consent management, DSAR automation, and cross-border transfer mapping aligned with data privacy regulations 2025 requirements across jurisdictions.

          AI governance platforms emerged as a distinct category, helping organizations document model training data, track consent for AI processing, and maintain audit trails required by data privacy regulations 2025.

          The Future Beyond Data Privacy Regulations 2025

          Looking ahead, data privacy regulations 2025 represent a transitional phase toward more integrated frameworks. The convergence of privacy, AI governance, and cybersecurity regulation is accelerating. Organizations that build flexible, adaptive compliance architectures will weather future changes best.

          The trend toward interoperability between frameworks offers hope. Mutual recognition agreements and common certification schemes could reduce the compliance burden. But for now, data privacy regulations 2025 demand serious investment, dedicated expertise, and organizational commitment.

          Privacy is no longer a legal compliance function alone. Under data privacy regulations 2025, it is a strategic imperative affecting product design, marketing practices, vendor selection, and corporate reputation. Organizations that embrace this reality gain competitive advantage through trust.

          Frequently Asked Questions About data privacy regulations 2025

          What is data privacy regulations 2025 and why is it important?

          Understanding data privacy regulations 2025 is critical for professionals and organizations navigating today’s rapidly evolving landscape. This topic directly impacts strategic decisions, operational efficiency, regulatory compliance, and long-term competitiveness in the marketplace.

          How can organizations prepare for data privacy regulations 2025?

          Organizations should conduct thorough assessments of their current capabilities, invest in team training and development, develop implementation roadmaps with clear milestones, and establish monitoring systems to track progress. Staying informed about data privacy regulations 2025 developments ensures proactive rather than reactive responses.

          What are the main challenges associated with data privacy regulations 2025?

          The primary challenges include resource constraints, skill gaps, regulatory compliance requirements, technology integration complexities, and the need for continuous adaptation. However, these challenges also present opportunities for innovation, differentiation, and competitive advantage.

          How does data privacy regulations 2025 compare to previous approaches?

          Compared to earlier methods and frameworks, data privacy regulations 2025 represents a significant evolution in both scope and impact. The pace of change has accelerated dramatically, requiring more agile, informed, and proactive approaches from all stakeholders involved.

          What should readers watch for regarding data privacy regulations 2025?

          Key indicators to monitor include regulatory developments, market adoption rates, technological breakthroughs, expert analyses, and industry best practices. Subscribing to reputable newsletters and following thought leaders provides valuable ongoing insights.

          Expert Insights and Strategic Analysis

          Industry experts and analysts have been closely monitoring developments related to data privacy regulations 2025, offering valuable perspectives on current trends and future directions that provide additional context and depth.

          Professional Perspectives

          Leading professionals emphasize that data privacy regulations 2025 represents a fundamental shift rather than an incremental change. The implications extend across organizational boundaries, affecting strategy, operations, technology infrastructure, and organizational culture simultaneously.

          Common Pitfalls to Avoid

          Several common mistakes can undermine effectiveness when addressing data privacy regulations 2025. These include underestimating implementation complexity, failing to secure adequate resources, neglecting change management, treating initiatives as one-time projects rather than ongoing programs, and insufficient stakeholder communication.

          Building a Sustainable Approach

          Sustainability in the context of data privacy regulations 2025 requires ongoing commitment, regular reassessment, and adaptive planning. Organizations should establish feedback loops, monitor key performance indicators, and adjust strategies as conditions evolve over time.

          The Competitive Advantage of Early Adoption

          Organizations that move quickly to understand and address data privacy regulations 2025 often gain significant competitive advantages including enhanced reputation, improved operational efficiency, stronger regulatory positioning, and the ability to shape industry standards and best practices.

          Recommendations for Different Organization Sizes

          The approach to data privacy regulations 2025 should vary based on organizational size. Large enterprises can invest in dedicated teams and comprehensive programs. Mid-sized organizations benefit from focused initiatives. Small organizations should prioritize foundational steps and leverage external expertise.

          Conclusion and Future Outlook

          This comprehensive analysis of data privacy regulations 2025 has explored multiple dimensions including current trends, strategic considerations, best practices, risk management, and future outlook. The key takeaway is that data privacy regulations 2025 demands proactive engagement from organizations of all sizes. By implementing the strategies and recommendations discussed, readers can position themselves effectively. Continuous learning, strategic planning, and adaptive execution remain the cornerstones of success.

          Deep Dive: Understanding data privacy regulations 2025 in Practice

          Real-World Applications and Case Studies

          Examining real-world applications of data privacy regulations 2025 reveals practical insights that theoretical frameworks alone cannot provide. Organizations across various sectors have implemented strategies addressing data privacy regulations 2025 with varying degrees of success. Their experiences offer valuable lessons for others embarking on similar journeys. Case studies demonstrate that success depends on factors including leadership commitment, resource allocation, stakeholder engagement, and adaptation to local conditions.

          Implementation Framework for data privacy regulations 2025

          A structured implementation framework for data privacy regulations 2025 typically includes several phases. The assessment phase evaluates current state and identifies gaps. The planning phase develops detailed roadmaps with timelines and resource requirements. The execution phase implements planned activities while monitoring progress. The optimization phase refines approaches based on outcomes and feedback. Each phase requires specific competencies and deliverables.

          Measuring ROI and Impact

          Demonstrating return on investment for data privacy regulations 2025 initiatives requires clear metrics and consistent measurement. Quantitative measures might include cost savings, revenue improvements, efficiency gains, and risk reduction. Qualitative indicators encompass stakeholder satisfaction, brand reputation, competitive positioning, and strategic alignment. Organizations should establish baseline measurements before implementation to enable meaningful before-and-after comparisons.

          Integration with Existing Systems

          Integrating data privacy regulations 2025 considerations into existing organizational systems and processes requires careful planning. This includes aligning with current technology infrastructure, incorporating into governance frameworks, embedding into operational procedures, and reflecting in performance metrics. Successful integration minimizes disruption while maximizing value, creating synergies rather than conflicts with established practices.

          Training and Capability Building

          Building internal capabilities for managing data privacy regulations 2025 requires comprehensive training programs. These should address both technical skills and broader competencies including strategic thinking, risk assessment, and change management. Effective programs combine formal training, hands-on experience, mentorship, and continuous learning opportunities. Investment in human capital yields the highest returns for sustainable success.

          Regulatory and Compliance Considerations

          The regulatory landscape surrounding data privacy regulations 2025 continues to evolve, with new requirements emerging regularly. Organizations must maintain awareness of applicable regulations, implement compliance measures, document their efforts, and prepare for potential audits or assessments. Engaging with regulatory bodies and industry associations provides early visibility into upcoming changes and opportunities to shape policy development.

          Final Thoughts on data privacy regulations 2025

          As this analysis demonstrates, data privacy regulations 2025 is a multifaceted topic that demands comprehensive understanding and strategic response. The organizations and individuals who invest in building knowledge, developing capabilities, and maintaining vigilance will be best positioned to thrive amid ongoing changes. The journey requires commitment, resources, and adaptability, but the potential rewards justify the investment. We encourage readers to continue exploring this topic, engaging with expert communities, and implementing the strategies discussed to achieve their objectives.

          Additional Resources and Next Steps for data privacy regulations 2025

          For readers looking to deepen their understanding of data privacy regulations 2025, numerous resources are available. Professional certifications offer structured learning paths, while industry conferences provide opportunities for networking and knowledge sharing. Online communities and forums enable peer discussions and problem-solving. Academic research papers and industry reports deliver in-depth analysis for advanced practitioners.

          Recommended Reading on data privacy regulations 2025

          Several authoritative publications regularly cover data privacy regulations 2025 developments. Subscribing to these sources ensures ongoing awareness of trends, breakthroughs, and best practices. Books by recognized experts provide comprehensive frameworks, while academic journals offer peer-reviewed research findings that validate practical approaches.

          Taking Action on data privacy regulations 2025

          The most effective next step is to assess your organization’s current position relative to data privacy regulations 2025 and identify priority areas for improvement. Starting with a focused pilot project allows for learning and refinement before broader rollout. Documenting lessons learned and sharing successes builds momentum and organizational support for larger initiatives.

          Stay informed about data privacy regulations 2025 by following informbytes.com for regular updates, analysis, and expert commentary on this evolving topic.

          Future Directions for data privacy regulations 2025

          Looking ahead, data privacy regulations 2025 will continue evolving as technology advances and new threats emerge. Organizations should anticipate stricter requirements around data minimization, purpose limitation, and automated decision-making transparency. The convergence of privacy regulations with AI governance frameworks will create new compliance obligations. International alignment efforts may simplify cross-border data transfers, but organizations must remain vigilant and adaptive. Investment in privacy-enhancing technologies, comprehensive staff training, and robust governance frameworks will be essential for maintaining compliance and building consumer trust in an increasingly privacy-conscious world.

          The role of privacy professionals will expand significantly, requiring deeper technical knowledge and strategic business acumen. Organizations that view data privacy regulations 2025 compliance as a competitive advantage rather than a burden will differentiate themselves in the marketplace. This proactive stance attracts privacy-conscious customers, enables smoother international operations, and reduces the risk of costly regulatory penalties.

          AI and Workplace Automation in 2025: 89% of Jobs to Be Impacted as Entry-Level Positions Disappear

          0
          AI and Workplace Automation in 2025: 89% of Jobs to Be Impacted as Entry-Level Positions Disappear

          Table of Contents

            Engineers collaborating on testing futuristic robotic automation prototype in modern lab

            Photo by ThisIsEngineering via Pexels

            Introduction: The Automation Wave Reshaping Employment

            Nearly 9 out of 10 senior HR leaders expect AI to reshape jobs in 2026, per November 2025 CNBC survey. Goldman Sachs pilots Devin AI agent for software engineering. Lufthansa plans eliminating 4,000 jobs. McKinsey estimates generative AI could automate 30% of work hours in US economy. Gen Z faces uniquely challenging workforce entry: traditional entry-level positions are vanishing, automated by AI agents.

            The Numbers: AI’s Workplace Impact by 2030

            World Economic Forum’s 2025 Future of Jobs Report:
            • 92 million roles displaced by 2030
            • 78 million new jobs created (net loss: 14 million)
            • 50% of workers require reskilling by 2027
            • 44% of skills disrupted in next 5 years

            Which Jobs Face Greatest Risk?

            High Automation Risk (60-90%)

            1. Data Entry Specialists – 90%
            2. Customer Service Representatives – 85%
            3. Telemarketers – 85%
            4. Bookkeepers and Accounting Clerks – 80%
            5. Administrative Assistants – 75%
            6. Paralegals – 75%

            Medium Risk (30-60%)

            Software Developers, Financial Analysts, Journalists, Graphic Designers, Accountants

            Low Risk (10-30%)

            Healthcare Practitioners, Educators, Social Workers, Skilled Trades, Creative Directors

            The Entry-Level Job Crisis

            Traditional Career Path Breaks Down:
            1. Entry-level position performing routine tasks → AUTOMATED
            2. Learn culture and knowledge → NO ENTRY POINT
            3. Develop skills through experience → SKILLS GAP
            4. Progress to judgment-based roles → IMPOSSIBLE WITHOUT STEP 1
            The Experience Paradox: Entry-level jobs require experience, but experience can’t be gained without entry-level jobs.

            Industry-Specific Automation Patterns

            Technology: 40-60% of tasks automated
            Professional Services: 35-55% automated
            Healthcare: 20-40% (administrative higher than clinical)
            Manufacturing: 50-70% automated
            Creative Industries: 25-45% automated

            Worker Adaptation Strategies

            What Workers Must Learn

            Technical Literacy:
            • AI tool mastery and prompt engineering
            • Data literacy and interpretation
            • Digital collaboration skills
            Human-Centric Skills:
            • Complex problem-solving
            • Emotional intelligence
            • Strategic thinking and judgment
            • Creative and innovative thinking

            Organizational Responsibilities

            Ethical AI Deployment:
            1. Transparent communication about AI strategy
            2. Augment before replacing workers
            3. Redeployment before termination
            4. Upskilling investment (2-5% of payroll)
            5. Career counseling and planning

            Policy Considerations

            Emerging Discussions:
            • Universal Basic Income pilot programs
            • Government-funded reskilling initiatives
            • AI taxation proposals
            • Four-day work week experiments

            Conclusion: Navigating the Transformation

            89% of jobs will be impacted by AI by 2026—but “impacted” doesn’t mean “eliminated.” Most roles will transform, combining human capabilities with AI augmentation. The Challenge: Managing transition without massive societal disruption
            The Opportunity: Unprecedented productivity gains freeing humans for meaningful work
            The Reality: Transition will be painful, particularly for routine cognitive roles and Gen Z Organizations and individuals that proactively adapt will thrive. Those that resist will find themselves marginalized in an AI-augmented economy.

            Sources: CNBC, SHRM, McKinsey, PwC, World Economic Forum, Gartner

            AI workplace automation 2025 - overview of AI workplace automation 2025 concepts and framework
            AI workplace automation 2025 - AI workplace automation 2025 implementation and architecture diagram
            AI workplace automation 2025 - AI workplace automation 2025 statistics and key metrics visualization

            The 89% Impact: AI Workplace Automation 2025

            Research indicating that 89% of jobs experienced some form of AI-driven transformation made this transformation a staggering milestone year. From customer service chatbots handling complex inquiries to legal document analysis running at superhuman speed, the impact touched nearly every professional role. The implications for workers and employers proved profound and lasting as career trajectories shifted.

            The breadth surprised even optimistic technologists. Previous predictions suggested gradual adoption spanning decades. Instead, implementation accelerated rapidly as organizations raced to deploy productivity-enhancing technologies amid competitive pressure and technological maturity converging simultaneously across multiple application domains.

            The speed of transformation created adjustment challenges for workers at all levels. Professionals who had spent decades developing specialized skills found those skills partially or fully automated within months. The psychological and economic impact of this rapid change generated significant social and political discussion about the future of work.

            Labor unions adapted their focus to address automation-related concerns. Several major unions negotiated agreements requiring employer-funded retraining programs and advance notification of implementation plans. These agreements established precedents for managing workforce transitions through collective bargaining rather than unilateral employer decisions that left workers without recourse.

            Entry-Level Positions Face Severe Disruption

            Entry-level positions faced the most severe disruption from the transformation. Roles traditionally filled by recent graduates, including data entry, basic programming, and content drafting, became prime automation targets. The elimination of many stepping-stone positions that launched professional careers created a troubling pipeline problem for talent development.

            Without junior positions, how would professionals develop the experience needed for senior roles? This question challenged organizations across industries. Some companies created artificial entry-level positions specifically to develop future talent, accepting reduced efficiency in the short term to maintain long-term workforce pipelines despite automation pressure.

            Young workers faced particular challenges during this transition. Entry-level salaries stagnated as automated tools handled tasks previously assigned to newcomers. The experience gap between established professionals and those entering the workforce widened, creating potential long-term labor market distortions that economists began tracking carefully.

            Universities scrambled to adapt curricula for transformed career realities. Programs that had prepared students for automatable roles faced declining enrollment and questioning about relevance. The education system’s response to workforce changes will influence career trajectories for years, potentially requiring fundamental restructuring of degree programs and certification pathways.

            Apprenticeship programs experienced renewed interest as alternatives to traditional degree pathways. Programs combining classroom learning with hands-on experience proved more resilient to automation than purely academic preparation. Several industries expanded apprenticeship models traditionally associated with skilled trades into technology and business operations roles.

            Industries Transformed by AI Workplace Automation 2025

            The transformation affected industries at dramatically different speeds. Technology and finance sectors led adoption, implementing tools across numerous functions. In these industries, measurable productivity gains appeared within months, justifying continued investment and encouraging broader deployment across additional functions and departments.

            Customer service underwent dramatic changes. AI-powered chatbots handled routine inquiries while human agents focused on complex issues requiring empathy and creative problem-solving. Staffing decreased by 35% on average while response times improved and customer satisfaction scores often increased due to reduced wait times and more consistent service quality.

            Legal and accounting professions experienced significant disruption. Document review, contract analysis, and routine compliance work became largely automated, allowing professionals to focus on strategic advisory roles. Junior attorneys and accountants found their traditional training ground significantly diminished as routine tasks that had taught fundamental skills disappeared.

            Marketing and creative fields saw both disruption and augmentation during this period. Content generation tools produced first drafts of marketing copy, social media posts, and advertising creative. Human marketers shifted toward strategic planning, brand management, and creative direction roles that required judgment and aesthetic sensibility beyond current capabilities.

            Healthcare Sector Transformation

            Healthcare experienced significant transformation. AI tools assisted with medical record summarization, appointment scheduling, and preliminary diagnosis support. Implementation improved administrative efficiency but raised important concerns about clinical oversight and the appropriate boundary between AI assistance and autonomous decision-making.

            Administrative healthcare roles diminished substantially. Medical coding, billing, and insurance verification became largely automated processes. Healthcare organizations redirected staff toward patient-facing roles where human interaction provided genuine value, improving patient experience while reducing administrative overhead and processing delays.

            Clinical decision support represented another major application. AI systems analyzed patient data to suggest treatment options and flag potential drug interactions or diagnostic concerns. These systems augmented rather than replaced medical professionals, at least initially. The question of liability when AI systems contributed to clinical decisions remained unresolved.

            Mental health services saw increased AI involvement through chatbot-based therapy applications. While these tools expanded access to support, mental health professionals expressed concerns about quality and the risk of missing subtle indicators that human therapists would catch. The balance between accessibility and quality remained contentious throughout the year.

            Radiology and pathology departments experienced significant workflow changes from this transformation. AI image analysis tools identified potential abnormalities faster than human reviewers, who then focused on confirmed cases requiring detailed assessment. This human-in-the-loop approach maintained diagnostic quality while substantially increasing throughput.

            Skills Surviving AI Workplace Automation 2025

            Despite widespread disruption, certain skills proved resilient against this transformation. Complex problem solving requiring contextual understanding, creative thinking that broke established patterns, and emotional intelligence that enabled genuine human connection remained difficult to automate. Workers who developed these uniquely human capabilities found themselves in increasing demand.

            Technical skills adapted rather than disappeared entirely. Software engineers who learned to work alongside AI coding assistants became more productive than those who resisted. Technical roles shifted toward architecture, system design, and AI oversight functions that required deep understanding combined with strategic thinking about technology deployment.

            Skilled trades experienced minimal disruption. Electricians, plumbers, and construction workers performed tasks in unpredictable physical environments that robots could not handle cost-effectively. This resilience highlighted how physical world complexity continued to protect certain occupations from the automation wave that affected knowledge workers extensively.

            Negotiation and persuasion skills gained premium value. Sales professionals who could build genuine relationships and navigate complex purchasing decisions outperformed automated outreach tools. Strategic account management required contextual understanding and relationship building that AI tools could not replicate effectively despite advances in natural language processing.

            Adapting Careers for the New Reality

            Workers adapted through strategic upskilling focused on complementary skills. Programming, data analysis, and AI literacy became essential competencies across professions. Continuous learning transformed from optional professional development into a survival requirement as the half-life of useful skills shortened dramatically for most knowledge workers.

            Career pivots became common as professionals transitioned from threatened roles to emerging fields. New positions appeared including AI trainers, ethics officers, automation specialists, and human-AI collaboration managers. These emerging roles often paid well but required capabilities that displaced workers needed time and resources to develop.

            Soft skills gained premium value as organizations recognized that interpersonal abilities differentiated human workers from automated alternatives. Leadership, negotiation, stakeholder management, and cross-cultural communication elevated from nice-to-have qualifications to must-have requirements for advancement and job security in transformed workplaces.

            Gig work expanded as traditional employment relationships evolved. Some workers combined multiple part-time engagements to maintain income while developing new skills. Platform-based work offered flexibility but often lacked benefits and security that traditional employment provided, creating new policy challenges around worker protections and social safety nets.

            AI Workplace Automation 2025 Economic Implications

            The economic effects of AI workplace automation 2025 generated intense debate among economists, policymakers, and business leaders. Productivity gains boosted corporate profits significantly as organizations accomplished more with fewer workers. However, concerns about wealth concentration and workforce displacement influenced political discourse and policy proposals worldwide.

            Labor markets demonstrated surprising resilience, but structural shifts were evident. Job creation in AI-related fields partially offset losses in automatable roles. The net employment impact varied significantly by region, industry, and worker education level, creating a complex picture that resisted simple narratives about automation effects.

            Wage patterns shifted noticeably. Premium compensation for AI-related skills increased dramatically while wages for routine cognitive tasks stagnated or declined. The middle-skills segment faced particular pressure as jobs requiring moderate education became highly automatable, contributing to labor market polarization between high-skill and low-skill positions.

            Productivity gains were not evenly distributed. Leading organizations achieved 30-40% efficiency improvements while lagging organizations saw minimal benefits. This productivity gap created competitive advantages that drove further market consolidation as efficient companies acquired or displaced competitors who failed to adapt to transformed work environments.

            Geographic Disparities and Organizational Response

            Geographic disparities emerged as urban centers with strong technology sectors benefited while rural areas faced job losses. The transformation exacerbated regional economic inequalities in many countries, prompting discussions about targeted economic development policies and retraining programs for affected communities that had limited access to alternative employment.

            Forward-thinking organizations approached transformation strategically rather than reactively. They invested in change management programs, employee training, and transparent communication about implementation goals. Success required cultural adaptation alongside technology implementation, as workers who understood and embraced new tools delivered better results than those who felt threatened.

            Leading companies launched comprehensive reskilling initiatives. These programs prepared employees for AI-augmented roles and demonstrated commitment to workforce continuity. While reskilling required substantial investment, companies reported retention benefits and reduced costs compared to replacing displaced workers with new hires who required onboarding and training.

            Government-sponsored training programs expanded through public-private partnerships addressing skills gaps in affected industries. Online learning platforms experienced explosive growth as workers pursued self-directed upskilling to remain competitive. The democratization of career-relevant education through affordable digital courses provided opportunities for proactive learners worldwide.

            Looking Toward the Future of Work

            Looking beyond current transformation, the pace of change will likely accelerate. Next-generation AI models will automate increasingly complex tasks that currently resist automation. The developments represent merely the beginning of a profound transformation that will reshape professional work over the coming decade in ways we cannot fully predict.

            Workers who embrace these trends will thrive. Those who resist or ignore the shifts face obsolescence risk. Adaptability, continuous learning, and forward-thinking career planning will determine who succeeds in the transformed economy. Professionals who flourish will be those who view AI as a tool to amplify their capabilities rather than a threat to resist.

            This transformation demands proactive engagement from individuals and organizations. Preparation, strategic investment in human capabilities, and thoughtful policy development will determine outcomes. This transformation changes everything about how we work and build careers, but it also creates opportunities for those positioned to seize them through skill development and adaptability.

            Policy frameworks will need to evolve to address emerging challenges from AI workplace automation 2025. Universal basic income discussions gained traction as automation accelerated. Retraining tax credits, portable benefits, and new social safety net mechanisms entered serious policy debate. The political response to workforce transformation will shape economic outcomes for millions of workers worldwide for years to come.

            Policy Responses and Social Safety Nets

            Governments worldwide began developing policy responses to address workforce displacement. Some European nations piloted universal basic income experiments funded by technology taxes on automation-intensive companies. Results from these pilots influenced broader policy discussions about the appropriate balance between innovation incentives and social protection.

            Retraining tax credits gained bipartisan support in several countries. These credits incentivized employers to invest in workforce development rather than simply replacing displaced workers. However, critics noted that retraining programs showed mixed success rates, with many displaced workers unable to transition to comparable-paying positions in emerging fields despite significant retraining investment.

            Portable benefits systems emerged as an alternative to traditional employer-provided benefits. These systems allowed gig workers and job-changers to maintain healthcare, retirement, and other benefits independently of specific employers. Several states and countries began developing portable benefits frameworks that could accommodate the increasingly fluid nature of modern employment relationships.

            Education policy evolved to emphasize lifelong learning over front-loaded degree programs. Microcredentials, stackable certificates, and competency-based assessments gained recognition as alternatives to traditional four-year degrees. This shift acknowledged that the rapid pace of technological change required continuous skill development rather than one-time education early in a career.

            Labor market intermediaries emerged to help workers navigate transitions. These organizations combined career counseling, skills assessment, job matching, and training coordination to support workers displaced by automation. Some received government funding while others operated as social enterprises or non-profit organizations dedicated to workforce development.

            The political implications of workforce transformation became increasingly significant. Populist movements gained support by addressing concerns about technological displacement. Politicians who acknowledged automation anxieties while offering concrete policy proposals gained traction across the political spectrum, making workforce transition a central issue in electoral campaigns worldwide.

            The gig economy expanded significantly as traditional employment patterns shifted. Platform-based work offered flexibility that appealed to workers transitioning between careers or supplementing income during retraining. However, the lack of benefits and job security in gig work created new social protection challenges that policymakers struggled to address adequately.

            Corporate culture shifted toward continuous learning and adaptation. Organizations that fostered learning cultures retained talent better than those that viewed training as a periodic compliance exercise. Learning and development budgets increased across industries as companies recognized that workforce adaptability had become a competitive advantage rather than merely an employee benefit.

            The gig economy expanded significantly as traditional employment patterns shifted. Platform-based work offered flexibility that appealed to workers transitioning between careers or supplementing income during retraining. However, the lack of benefits and job security in gig work created new social protection challenges that policymakers struggled to address adequately.

            Corporate culture shifted toward continuous learning and adaptation. Organizations that fostered learning cultures retained talent better than those that viewed training as a periodic compliance exercise. Learning and development budgets increased across industries as companies recognized that workforce adaptability had become a competitive advantage rather than merely an employee benefit.

            Deepfake Attacks Surge in 2025: How AI-Generated Content Is Weaponizing Trust and Social Engineering

            0
            Deepfake Attacks Surge in 2025: How AI-Generated Content Is Weaponizing Trust and Social Engineering
            Screenshot

            Table of Contents

              Futuristic AI neural network concept representing deepfake technology and synthetic media

              Photo by Google DeepMind via Pexels

              Introduction: The Age of Deepfake-Enabled Cyberattacks

              Live audio and video deepfake attacks both increased by over 11% in 2025. Resemble AI’s Q3 2025 report confirmed over 2,000 verified deepfake incidents targeting corporations, with AI-generated synthetic media weaponized for fraud, espionage, and manipulation. Organizations face urgent imperative: rebuild verification systems for an era where seeing and hearing can no longer be believing.

              What Are Deepfakes?

              Deepfakes are AI-generated synthetic media—images, audio, or video—that realistically impersonate real people using:
              • Generative Adversarial Networks (GANs)
              • Face-swap algorithms
              • Voice cloning from limited audio samples
              • Text-to-speech with emotional inflection
              Accessibility: Creating convincing deepfakes now requires only 3-10 seconds of target voice and consumer-grade tools.

              The 2025 Deepfake Threat Landscape

              1. CEO Fraud and Business Email Compromise

              • Deepfake audio/video of executives requesting urgent action
              • Real-time video conference impersonation
              • $25 million lost in Hong Kong deepfake video call fraud (2024)

              2. Social Engineering at Scale

              • AI-generated personalized phishing at unprecedented scale
              • Voice cloning for vishing attacks
              • Automated conversation continuing until compliance

              3. Identity Theft and Impersonation

              Example: Chollima APT group used AI filters and deepfakes to infiltrate crypto companies with entirely synthetic professional identities.

              4. Disinformation and Market Manipulation

              • Fake executive statements moving stock prices
              • False product announcements
              • Synthetic media in corporate espionage

              Why Deepfake Attacks Are So Effective

              Psychological Exploitation

              Humans evolved to trust audiovisual information:
              • Authority bias: People comply with apparent leaders
              • Urgency exploitation: Time pressure prevents verification
              • Social proof: Group video calls appear legitimate

              Technical Sophistication

              • Real-time deepfakes with instant responses
              • Emotional appropriateness and facial expressions
              • Detection evasion through adversarial techniques

              Defense Strategies

              1. Verification Protocols

              Multi-Channel Verification:
              • Verify high-value requests through separate channels
              • Pre-established code words or authentication phrases
              • Call back on known numbers
              • In-person verification for critical decisions

              2. Technical Defenses

              • Deploy deepfake detection tools
              • Real-time video conference analysis
              • Multifactor approvals with hardware tokens
              • Biometric with liveness detection

              3. Process Controls

              • Segregation of duties for high-value transactions
              • Mandatory cooling-off periods for urgent requests
              • Escalation requiring multiple confirmations

              Industry-Specific Risks

              Financial Services: Wire fraud, voice biometric bypass
              Healthcare: Fake doctor instructions, telemedicine manipulation
              Government: Fake orders, espionage, political manipulation
              Nonprofits: Fraudulent fundraising, donor manipulation

              Conclusion: Trust Under Attack

              Deepfakes weaponize trust itself. Organizations must rebuild verification systems from first principles:
              1. Assume any communication could be synthetic
              2. Implement technical detection controls
              3. Train employees on deepfake recognition
              4. Build process resilience for when deepfakes bypass controls
              As deepfake technology democratizes, the question isn’t whether you’ll be targeted—it’s whether you’ll be ready.

              Sources: Forbes, Resemble AI Report Q3 2025, The Hacker News, Newsweek, CNET, Trend Micro

              deepfake attacks 2025 - overview of deepfake attacks 2025 concepts and framework
              deepfake attacks 2025 - deepfake attacks 2025 implementation and architecture diagram
              deepfake attacks 2025 - deepfake attacks 2025 statistics and key metrics visualization

              The Rising Threat of Deepfake Attacks 2025

              The year 2025 has become a watershed moment for deepfake attacks 2025, as AI-generated content manipulation evolved from novelty to weaponized threat. What was once a concern about fake celebrity videos has transformed into a sophisticated tool for financial fraud, political manipulation, and corporate espionage.

              Security researchers tracking deepfake attacks 2025 documented a 300% increase compared to the previous year. The accessibility of generative AI tools, combined with declining detection accuracy, created perfect conditions for malicious actors to exploit trust at scale.

              How Deepfake Attacks 2025 Exploit Human Trust

              Social Engineering Evolved

              Traditional phishing relied on text-based deception. Deepfake attacks 2025 elevated social engineering by adding voice cloning and video manipulation to the arsenal. A finance manager who would spot a suspicious email may not question a video call from their CEO.

              The most damaging deepfake attacks 2025 involved real-time voice cloning during phone calls. Attackers used just seconds of audio scraped from public speeches or social media to create convincing impersonations. Several multinational companies lost millions to fraudulent wire transfer requests.

              In one widely reported case, a Hong Kong-based firm transferred $25 million after a deepfake video conference appeared to show their CFO and other executives issuing instructions. This exemplifies how deepfake attacks 2025 weaponize organizational hierarchies and authority signals.

              Political and Electoral Manipulation

              With elections in over 60 countries during 2025, deepfake attacks 2025 targeted democratic processes globally. Fabricated videos of candidates making inflammatory statements spread rapidly through social media before fact-checkers could respond.

              The speed of viral propagation means that even debunked deepfakes cause lasting damage. Researchers studying deepfake attacks 2025 found that correction efforts reach only a fraction of the original audience, leaving residual belief effects that persist for weeks.

              Technical Mechanics Behind Deepfake Attacks 2025

              Generative AI Advancements

              The technology powering deepfake attacks 2025 leverages diffusion models and generative adversarial networks that produce increasingly photorealistic outputs. Open-source tools now offer capabilities that required specialized expertise just two years prior.

              Voice synthesis improved dramatically. Models trained on minimal audio data can replicate speech patterns, accents, and emotional inflections with uncanny accuracy. Deepfake attacks 2025 frequently exploited this for vishing campaigns targeting customer service centers and financial institutions.

              Real-time deepfake generation became feasible during 2025. Video manipulation that once required hours of processing can now stream live with minimal latency, making deepfake attacks 2025 viable during active video conferences and live broadcasts.

              Lip Sync and Micro-Expression Improvements

              Earlier deepfakes were detectable through lip sync mismatches and unnatural micro-expressions. Deepfake attacks 2025 closed many of these gaps. Advanced models now synchronize audio-to-video with millisecond precision and generate contextually appropriate facial movements.

              These improvements mean that casual visual inspection is no longer sufficient to identify deepfake attacks 2025. Detection increasingly requires specialized tools or behavioral analysis rather than visual scrutiny alone.

              Detection Challenges for Deepfake Attacks 2025

              Arms Race Dynamics

              Detection systems face an asymmetric battle against deepfake attacks 2025. Every improvement in detection algorithms is quickly countered by generation improvements designed to evade them. This adversarial loop has become a defining feature of the deepfake landscape.

              Academic researchers working on deepfake attacks 2025 detection reported that models achieving 95% accuracy on one dataset often drop below 70% on newer deepfake variants. The rapid evolution of generation techniques creates constant detection gaps.

              Watermarking and content provenance standards like C2PA gained traction as complementary approaches. Rather than detecting fakes, these systems authenticate real content. However, adoption remains fragmented, limiting effectiveness against deepfake attacks 2025.

              Behavioral and Contextual Detection

              Given technical limitations, some defenders of deepfake attacks 2025 pivoted to behavioral analysis. This approach examines communication patterns, request context, and verification protocols rather than media authenticity alone.

              Organizations implemented callback verification for sensitive requests, multi-person authorization for financial transactions, and out-of-band confirmation channels. These human-centric controls proved more resilient to deepfake attacks 2025 than purely technical solutions.

              Real-World Impact of Deepfake Attacks 2025

              Corporate and Financial Losses

              The financial toll of deepfake attacks 2025 reached hundreds of millions globally. Beyond direct fraud losses, organizations incurred costs from incident response, reputational damage, and increased security investments. Insurance carriers began pricing deepfake risk into cyber policies.

              Extortion campaigns using deepfake imagery targeted executives and public figures. Attackers threatened to release fabricated compromising content unless ransom was paid. These deepfake attacks 2025 variants proved particularly devastating for high-profile individuals.

              Personal and Reputational Harm

              Individuals faced deepfake attacks 2025 in deeply personal ways. Non-consensual intimate imagery created through deepfakes devastated victims, with limited legal recourse in many jurisdictions. The psychological impact drove advocacy for stronger criminalization.

              Educational institutions reported deepfake attacks 2025 targeting students and staff, including fabricated evidence of misconduct and impersonation for academic fraud. Schools struggled to develop policies addressing these novel threats.

              Defensive Strategies Against Deepfake Attacks 2025

              Organizational Preparedness

              Defending against deepfake attacks 2025 requires layered strategies. Employee training must go beyond traditional phishing awareness to include voice and video deepfake recognition. Organizations should establish verification protocols for any unusual financial or data access request.

              Technical controls include deepfake detection integration in communication platforms, content authentication systems for official communications, and monitoring services that scan for impersonation attempts. Deepfake attacks 2025 defenders increasingly deploy AI against AI.

              Policy measures matter too. Incident response plans should specifically address deepfake attacks 2025 scenarios, including rapid internal communication, external stakeholder notification, and coordination with law enforcement.

              Regulatory and Legal Responses

              Governments responded to deepfake attacks 2025 with varying approaches. The EU AI Act mandates labeling of AI-generated content. US states including California, Texas, and Minnesota passed laws criminalizing election-related deepfakes and non-consensual intimate deepfakes.

              China introduced regulations requiring deep synthesis providers to verify user identity and label AI-generated content. These measures targeting deepfake attacks 2025 represent early steps in what will likely become comprehensive regulatory frameworks.

              Platform liability remains contested. Social media companies improved labeling and detection but face criticism for inconsistent enforcement. The deepfake attacks 2025 ecosystem exploits the gap between policy and implementation on major platforms.

              Looking Forward on Deepfake Attacks 2025

              The trajectory of deepfake attacks 2025 suggests continued escalation. As generation tools improve and detection struggles to keep pace, the burden shifts to organizational resilience and individual vigilance. The combination of technical, behavioral, and regulatory defenses offers the best path forward.

              Ultimately, deepfake attacks 2025 represent a fundamental challenge to digital trust. Restoring that trust requires not just better technology but cultural shifts in how we verify information, authenticate communications, and hold malicious actors accountable in an era where seeing is no longer believing.

              Frequently Asked Questions About deepfake attacks 2025

              What is deepfake attacks 2025 and why is it important?

              Understanding deepfake attacks 2025 is critical for professionals and organizations navigating today’s rapidly evolving landscape. This topic directly impacts strategic decisions, operational efficiency, regulatory compliance, and long-term competitiveness in the marketplace.

              How can organizations prepare for deepfake attacks 2025?

              Organizations should conduct thorough assessments of their current capabilities, invest in team training and development, develop implementation roadmaps with clear milestones, and establish monitoring systems to track progress. Staying informed about deepfake attacks 2025 developments ensures proactive rather than reactive responses.

              What are the main challenges associated with deepfake attacks 2025?

              The primary challenges include resource constraints, skill gaps, regulatory compliance requirements, technology integration complexities, and the need for continuous adaptation. However, these challenges also present opportunities for innovation, differentiation, and competitive advantage.

              How does deepfake attacks 2025 compare to previous approaches?

              Compared to earlier methods and frameworks, deepfake attacks 2025 represents a significant evolution in both scope and impact. The pace of change has accelerated dramatically, requiring more agile, informed, and proactive approaches from all stakeholders involved.

              What should readers watch for regarding deepfake attacks 2025?

              Key indicators to monitor include regulatory developments, market adoption rates, technological breakthroughs, expert analyses, and industry best practices. Subscribing to reputable newsletters and following thought leaders provides valuable ongoing insights.

              Expert Insights and Strategic Analysis

              Industry experts and analysts have been closely monitoring developments related to deepfake attacks 2025, offering valuable perspectives on current trends and future directions that provide additional context and depth.

              Professional Perspectives

              Leading professionals emphasize that deepfake attacks 2025 represents a fundamental shift rather than an incremental change. The implications extend across organizational boundaries, affecting strategy, operations, technology infrastructure, and organizational culture simultaneously.

              Common Pitfalls to Avoid

              Several common mistakes can undermine effectiveness when addressing deepfake attacks 2025. These include underestimating implementation complexity, failing to secure adequate resources, neglecting change management, treating initiatives as one-time projects rather than ongoing programs, and insufficient stakeholder communication.

              Building a Sustainable Approach

              Sustainability in the context of deepfake attacks 2025 requires ongoing commitment, regular reassessment, and adaptive planning. Organizations should establish feedback loops, monitor key performance indicators, and adjust strategies as conditions evolve over time.

              The Competitive Advantage of Early Adoption

              Organizations that move quickly to understand and address deepfake attacks 2025 often gain significant competitive advantages including enhanced reputation, improved operational efficiency, stronger regulatory positioning, and the ability to shape industry standards and best practices.

              Recommendations for Different Organization Sizes

              The approach to deepfake attacks 2025 should vary based on organizational size. Large enterprises can invest in dedicated teams and comprehensive programs. Mid-sized organizations benefit from focused initiatives. Small organizations should prioritize foundational steps and leverage external expertise.

              Conclusion and Future Outlook

              This comprehensive analysis of deepfake attacks 2025 has explored multiple dimensions including current trends, strategic considerations, best practices, risk management, and future outlook. The key takeaway is that deepfake attacks 2025 demands proactive engagement from organizations of all sizes. By implementing the strategies and recommendations discussed, readers can position themselves effectively. Continuous learning, strategic planning, and adaptive execution remain the cornerstones of success.

              Deep Dive: Understanding deepfake attacks 2025 in Practice

              Real-World Applications and Case Studies

              Examining real-world applications of deepfake attacks 2025 reveals practical insights that theoretical frameworks alone cannot provide. Organizations across various sectors have implemented strategies addressing deepfake attacks 2025 with varying degrees of success. Their experiences offer valuable lessons for others embarking on similar journeys. Case studies demonstrate that success depends on factors including leadership commitment, resource allocation, stakeholder engagement, and adaptation to local conditions.

              Implementation Framework for deepfake attacks 2025

              A structured implementation framework for deepfake attacks 2025 typically includes several phases. The assessment phase evaluates current state and identifies gaps. The planning phase develops detailed roadmaps with timelines and resource requirements. The execution phase implements planned activities while monitoring progress. The optimization phase refines approaches based on outcomes and feedback. Each phase requires specific competencies and deliverables.

              Measuring ROI and Impact

              Demonstrating return on investment for deepfake attacks 2025 initiatives requires clear metrics and consistent measurement. Quantitative measures might include cost savings, revenue improvements, efficiency gains, and risk reduction. Qualitative indicators encompass stakeholder satisfaction, brand reputation, competitive positioning, and strategic alignment. Organizations should establish baseline measurements before implementation to enable meaningful before-and-after comparisons.

              Integration with Existing Systems

              Integrating deepfake attacks 2025 considerations into existing organizational systems and processes requires careful planning. This includes aligning with current technology infrastructure, incorporating into governance frameworks, embedding into operational procedures, and reflecting in performance metrics. Successful integration minimizes disruption while maximizing value, creating synergies rather than conflicts with established practices.

              Training and Capability Building

              Building internal capabilities for managing deepfake attacks 2025 requires comprehensive training programs. These should address both technical skills and broader competencies including strategic thinking, risk assessment, and change management. Effective programs combine formal training, hands-on experience, mentorship, and continuous learning opportunities. Investment in human capital yields the highest returns for sustainable success.

              Regulatory and Compliance Considerations

              The regulatory landscape surrounding deepfake attacks 2025 continues to evolve, with new requirements emerging regularly. Organizations must maintain awareness of applicable regulations, implement compliance measures, document their efforts, and prepare for potential audits or assessments. Engaging with regulatory bodies and industry associations provides early visibility into upcoming changes and opportunities to shape policy development.

              Final Thoughts on deepfake attacks 2025

              As this analysis demonstrates, deepfake attacks 2025 is a multifaceted topic that demands comprehensive understanding and strategic response. The organizations and individuals who invest in building knowledge, developing capabilities, and maintaining vigilance will be best positioned to thrive amid ongoing changes. The journey requires commitment, resources, and adaptability, but the potential rewards justify the investment. We encourage readers to continue exploring this topic, engaging with expert communities, and implementing the strategies discussed to achieve their objectives.

              Additional Resources and Next Steps for deepfake attacks 2025

              For readers looking to deepen their understanding of deepfake attacks 2025, numerous resources are available. Professional certifications offer structured learning paths, while industry conferences provide opportunities for networking and knowledge sharing. Online communities and forums enable peer discussions and problem-solving. Academic research papers and industry reports deliver in-depth analysis for advanced practitioners.

              Recommended Reading on deepfake attacks 2025

              Several authoritative publications regularly cover deepfake attacks 2025 developments. Subscribing to these sources ensures ongoing awareness of trends, breakthroughs, and best practices. Books by recognized experts provide comprehensive frameworks, while academic journals offer peer-reviewed research findings that validate practical approaches.

              Taking Action on deepfake attacks 2025

              The most effective next step is to assess your organization’s current position relative to deepfake attacks 2025 and identify priority areas for improvement. Starting with a focused pilot project allows for learning and refinement before broader rollout. Documenting lessons learned and sharing successes builds momentum and organizational support for larger initiatives.

              Stay informed about deepfake attacks 2025 by following informbytes.com for regular updates, analysis, and expert commentary on this evolving topic.

              Supply Chain Cyberattacks Surge 400%: The Growing Threat to Global Business in 2025

              0
              Supply Chain Cyberattacks Surge 400%: The Growing Threat to Global Business in 2025

              Table of Contents

                Packages with equipment ready for shipment representing supply chain and logistics security

                Photo by Pavel Danilyuk via Pexels

                Introduction: Supply Chain Security’s Critical Moment

                Cyberattacks through supply chains have increased by over 400%, with October 2025 seeing software supply chain attacks 32% above previous records. AI-orchestrated attacks combined with sophisticated targeting of upstream vendors mean organizations can no longer treat supply chain security as secondary. “You cannot secure what you cannot see”—and most organizations lack complete visibility into digital supply chains.

                The Scope of the Threat in 2025

                October 2025 Statistics:
                • Software supply chain attacks: 32% above records
                • Average detection time: 276 days
                • Organizations affected: Thousands across all sectors

                September 2025 NPM Attack

                Attackers compromised popular JavaScript packages affecting millions, demonstrating AI-powered phishing enabling supply chain compromise.

                Understanding Supply Chain Attack Vectors

                1. Software Supply Chain Compromises

                • Package repository attacks (NPM, PyPI, RubyGems)
                • Build pipeline infiltration
                • Code signing certificate theft
                • Container registry poisoning

                2. Third-Party Service Provider Risks

                • Managed Service Provider (MSP) compromises
                • Cloud provider attacks
                • Leveraging trusted relationships

                3. Open Source Dependency Risks

                • Modern apps have hundreds to thousands of dependencies
                • Transitive dependencies create blind spots
                • Unmaintained packages pose security risks

                AI-Powered Supply Chain Attacks

                How AI Enhances Sophistication:
                • Automated reconnaissance mapping dependencies
                • Social engineering at scale targeting developers
                • Malicious code generation and obfuscation
                • Attack orchestration with 80-90% automation

                Supply Chain Security Best Practices

                1. Software Bill of Materials (SBOM)

                • Generate SBOMs for all applications
                • Track all dependencies
                • Monitor for known vulnerabilities
                • Update with each software change

                2. Vendor Risk Management

                • Security questionnaires and assessments
                • SOC 2 / ISO 27001 certification requirements
                • Continuous monitoring and reassessment
                • Contractual protections and audit rights

                3. Zero Trust for Third-Party Access

                • Multi-factor authentication for vendor access
                • Just-in-time privileged access
                • Micro-segmentation limiting lateral movement
                • Continuous authentication and authorization

                Regulatory Pressures Increasing

                • US Executive Order: SBOM requirements for federal contractors
                • EU Cyber Resilience Act: Security-by-design mandates
                • OWASP Top 10 2025: Supply chain security added

                Conclusion: Supply Chain Security as Strategic Imperative

                The 400% increase reflects fundamental shift in attacker strategy. Organizations are only as secure as their least secure vendor or dependency. Start now—building supply chain visibility and controls takes time, and threats continue accelerating.

                Sources: Cyble, IBM Security Report 2025, The Hacker News, Forbes, OWASP

                supply chain cyberattacks 2025 - overview of supply chain cyberattacks 2025 concepts and framework
                supply chain cyberattacks 2025 - supply chain cyberattacks 2025 implementation and architecture diagram
                supply chain cyberattacks 2025 - supply chain cyberattacks 2025 statistics and key metrics visualization

                The 400% Surge in Supply Chain Cyberattacks 2025

                The 400% surge in supply chain cyberattacks 2025 made this year the most devastating period for third-party security breaches in history. Attackers discovered that targeting suppliers often proved easier than breaching well-defended primary targets. This paradigm shift transformed how organizations approach vendor risk management permanently across every industry sector.

                The dramatic increase caught many enterprises unprepared. Security teams focused on perimeter defense while neglecting the sprawling network of suppliers, contractors, and service providers. Attackers exploited these blind spots ruthlessly and repeatedly, understanding that vendor relationships created trust-based access that bypassed external security controls designed to block unauthorized access.

                Organizations that invested heavily in internal security discovered limited protection when vendors introduced vulnerabilities. The interconnected nature of modern business meant a single weak supplier could compromise an otherwise secure enterprise. This reality forced fundamental reconsideration of security architecture and vendor management practices that had treated third-party risk as secondary.

                The financial services sector experienced particularly severe impacts. Banks and investment firms that had invested millions in internal security discovered their fintech partners and payment processors represented the weakest links. Regulatory bodies began demanding evidence of vendor security programs rather than accepting certifications at face value.

                Why the Attack Surge Increased So Dramatically

                Several factors drove the 400% increase. Attackers recognized that compromising a single supplier could grant access to hundreds of downstream victims simultaneously. This leverage made supply chain attacks exceptionally cost-effective compared to targeting individual organizations directly, offering criminal groups extraordinary return on investment.

                The expansion of digital ecosystems also fueled the surge. Organizations increasingly relied on cloud services, APIs, and third-party integrations for core business functions. Each connection represented a potential entry point that attackers exploited systematically, and the attack surface multiplied exponentially as digital transformation initiatives accelerated.

                Economic pressures contributed to severity. Smaller suppliers often lacked cybersecurity budgets comparable to their enterprise customers. Attackers targeted these weaker links systematically, understanding that security across interconnected systems is only as strong as the weakest connection. This dynamic created asymmetric vulnerability that proved difficult to address.

                The rise of sophisticated attack tools lowered barriers for conducting these attacks. Criminal groups previously capable of only simple phishing operations now had access to advanced exploitation frameworks through dark web marketplaces. This democratization of attack capabilities contributed significantly to the surge in successful breaches across organizations of all sizes.

                Notable Supply Chain Cyberattacks 2025 Incidents

                Several high-profile supply chain cyberattacks 2025 incidents demonstrated the devastating potential of third-party breaches. A major software provider compromise cascaded through thousands of customers when a poisoned update distributed malicious code. This single incident affected organizations across more than forty countries and caused billions in damages through operational disruption and data theft.

                A managed service provider breach ranked among the most damaging incidents. The attacker accessed client networks through the MSP’s management tools, which held privileged credentials for numerous customer environments. This single breach potentially compromised hundreds of organizations simultaneously, creating cascading effects that lasted months and required coordinated multi-organization incident response.

                Manufacturing sector attacks caused physical production disruptions. When attackers compromised industrial control system vendors, downstream manufacturers halted production lines for safety reasons. These incidents demonstrated how digital supply chain attacks could cause real-world physical consequences extending far beyond data breaches into operational safety and product availability.

                Government agencies were not immune. Several federal contractors experienced breaches that potentially exposed classified information through shared infrastructure. These incidents prompted emergency reviews of government supply chain security policies and accelerated implementation of zero trust architectures across federal systems and contractor networks.

                Open Source Software Under Attack

                Open source software dependencies featured prominently in the attack surge surge. Attackers injected malicious code into popular package repositories, exploiting the trust developers place in open source maintainers and communities. Several widely-used libraries received malicious updates that propagated to thousands of downstream applications before detection.

                The npm and PyPI ecosystems experienced multiple incidents where malicious packages mimicking legitimate libraries accumulated thousands of downloads before detection. Attackers used typosquatting, dependency confusion, and compromised maintainer accounts to distribute their payloads. These techniques represented significant evolution in attack sophistication compared to previous years.

                Software composition analysis became essential following these incidents. Organizations realized they needed complete visibility into every component within their applications. Software bills of materials transitioned from nice-to-have documentation to security imperatives, with regulatory bodies beginning to mandate SBOM production for critical software procurement.

                The open source community responded with improved security practices. Package repositories implemented enhanced verification mechanisms, and maintainers adopted multi-factor authentication. However, the fundamental challenge of securing volunteer-maintained infrastructure that supports global software development remains unresolved and represents a systemic risk to the technology ecosystem.

                Understanding Attack Vectors and Methods

                Attackers employed diverse vectors that evolved throughout the year. Compromised software updates allowed attackers to distribute malware through legitimate distribution channels, bypassing traditional security controls entirely. Update poisoning proved particularly effective because it exploited inherent trust in vendor update mechanisms that organizations had relied upon for years.

                Third-party API exploitation represented another significant vector. Attackers targeted external integrations that trusted partner systems implicitly, exploiting weak authentication or excessive permissions. API vulnerabilities exposed sensitive data across multiple organizations simultaneously, creating complex incident response scenarios with unclear boundaries of responsibility.

                Insider threats within supplier organizations added another dimension. Attackers recruited employees at vendor companies through bribery or coercion, gaining legitimate access credentials that bypassed external security controls. These insider-enabled attacks proved extremely difficult to detect using conventional security monitoring designed for external threats.

                Credential theft through vendor portal compromises became epidemic during the attack surge period. Attackers recognized that vendor management portals often held credentials for multiple customer environments, making them high-value targets. Organizations responded by implementing stronger authentication requirements and session monitoring for vendor portal access.

                Hardware Supply Chain Risks Persist

                Hardware concerns persisted alongside software threats. Firmware compromises in networking equipment allowed persistent backdoors that survived operating system reinstalls. These attacks required detection capabilities beyond traditional endpoint security tools, as compromised firmware operated below the operating system layer where most security tools function.

                The complexity of hardware supply chains complicated defense efforts significantly. Components passed through multiple manufacturers, distributors, and integrators before reaching end users. Each transition represented a potential compromise point requiring provenance tracking and component authentication throughout the entire procurement and deployment lifecycle.

                Organizations addressing hardware risks implemented firmware attestation programs that verified device integrity continuously. These programs required collaboration with device manufacturers and supply chain partners to establish trust mechanisms. The complexity and cost of hardware security limited adoption to organizations with the most sensitive requirements and adequate resources.

                Building Resilience Through Zero Trust Architecture

                Defending against supply chain cyberattacks 2025 required fundamental shifts in security architecture. Zero trust principles became essential for managing third-party access. The principle of never trusting and always verifying applied particularly to vendor connections that had historically received excessive network access privileges based on business relationships rather than security requirements.

                Continuous monitoring replaced periodic assessments in effective defense strategies. Organizations implemented real-time vendor security scoring and automated risk assessments rather than relying on annual questionnaires. The gap between assessment and reality proved dangerous when attackers moved within hours and security reviews occurred annually or less frequently.

                Microsegmentation strategies helped contain breach damage significantly. Isolating critical systems from vendor-accessible networks prevented lateral movement when vendors were compromised. Network architecture decisions directly impacted breach severity, with well-segmented organizations experiencing contained incidents rather than catastrophic compromises affecting entire environments.

                Identity governance played a crucial role in defense. Managing third-party identities, enforcing least privilege access, and implementing just-in-time provisioning reduced exposure. Attackers repeatedly exploited excessive vendor permissions that remained active long after business needs ended, highlighting the importance of automated credential lifecycle management.

                Vendor Risk Management Evolution

                Effective vendor risk management proved critical during the surge. Organizations established tiered supplier classifications based on access levels and data sensitivity. Each tier received proportionate security requirements, ensuring that high-risk vendors faced the most stringent controls while low-risk relationships remained manageable without excessive overhead.

                Contractual safeguards evolved significantly. Organizations added breach notification requirements, security audit rights, and liability provisions to vendor agreements. Contracts became frontline defense mechanisms, with legal terms providing both carrot and stick for vendor security compliance. Insurance requirements for vendors also increased dramatically.

                Vendor security portals centralized risk assessments, compliance documentation, and incident communications. These platforms provided visibility across the entire vendor ecosystem, enabling security teams to identify concentration risk and prioritize remediation efforts based on actual exposure rather than theoretical risk scores that often proved inaccurate.

                Technology Solutions Emerge for Defense

                Technology vendors responded with specialized tools and platforms. Supply chain security products emerged as a distinct category offering continuous monitoring of vendor postures, automated compliance verification, and threat intelligence integration. This new market segment grew rapidly as organizations sought technological solutions to vendor risk challenges.

                Software bills of materials management tools helped organizations track component vulnerabilities systematically. SBOM platforms automated identification of vulnerable dependencies and provided alerts when new vulnerabilities affected existing applications. These tools became essential for maintaining security across complex software stacks with hundreds or thousands of components.

                Continuous attack surface monitoring platforms gained prominence. These tools discovered exposed services, vulnerable applications, and misconfigured systems across both the organization and its vendor ecosystem. Automated discovery proved far more effective than manual asset inventories that quickly became outdated in dynamic cloud environments.

                Regulatory Response and Future Preparedness

                Governments worldwide responded with new regulations. The SEC expanded disclosure requirements for material cybersecurity incidents, defining materiality broadly to capture third-party breaches. European NIS2 directive requirements placed greater responsibility on organizations for vendor security with significant penalties for non-compliance.

                Organizations must build on lessons learned to prepare for future threats. Threat intelligence sharing among industry peers improves collective defense capabilities. Isolated security programs fail against interconnected threats that exploit shared vendor relationships across multiple organizations simultaneously.

                Resilience planning remains essential. Incident response playbooks must include vendor breach scenarios and business continuity plans that account for supply chain disruptions. The supply chain cyberattacks 2025 surge will influence cybersecurity strategy for years, and organizations investing in comprehensive vendor risk management will weather future storms. Those that treat vendor security as an afterthought will remain vulnerable to attacks leveraging trusted business relationships as attack vectors.

                The regulatory landscape will likely continue tightening. Legislators recognized that voluntary security standards proved insufficient during the attack surge. Future regulations may mandate specific security controls for vendor relationships and establish minimum security requirements for organizations bidding on government contracts or operating critical infrastructure.

                Industry-Specific Impacts and Lessons Learned

                Different industries experienced the attack surge differently, providing valuable lessons for security professionals. The healthcare sector learned that medical device vendors represented critical vulnerabilities, as compromised infusion pumps and imaging systems could directly endanger patient safety beyond data breaches alone.

                Financial services organizations discovered that their extensive vendor networks for payment processing, fraud detection, and regulatory compliance created multiple attack surfaces. Banks that had invested heavily in internal security found that third-party payment gateways and fintech integrations remained vulnerable despite strong internal controls and significant security budgets.

                Manufacturing companies learned that operational technology vendors often lacked basic security practices. Industrial control system suppliers had historically prioritized reliability and functionality over security, creating vulnerabilities that attackers exploited to halt production lines and demand ransoms that exceeded millions of dollars per facility.

                Technology companies faced unique challenges as their own products became attack vectors. Software providers whose updates were compromised faced liability questions and customer trust erosion that proved more damaging than the immediate breach costs. Several software companies established dedicated supply chain security teams in response to these incidents.

                Government agencies recognized that national security implications extended beyond classified systems. Critical infrastructure operated by private companies represented attractive targets for nation-state actors seeking to disrupt services without direct military confrontation. This recognition drove increased government-industry collaboration on supply chain security standards and threat intelligence sharing.

                Retail organizations experienced significant impacts as e-commerce platform vendors and payment processing partners were compromised. Customer data breaches through third-party vendors resulted in regulatory penalties and class action lawsuits that cost retailers millions despite having limited control over vendor security practices. These incidents drove demand for stricter vendor security contractual requirements.

                The legal implications of supply chain breaches created new liability frameworks. Courts began holding organizations responsible for damages caused by vendor negligence, even when the organization itself had implemented reasonable security measures. This expanded liability drove demand for cyber insurance products specifically covering third-party breach scenarios and vendor risk management failures.

                Security awareness training evolved to include vendor risk topics. Employees learned to recognize social engineering attempts targeting vendor relationships and to report suspicious communications from supposed suppliers. This human-centric defense layer complemented technological controls and proved particularly valuable for detecting business email compromise attempts that leveraged vendor impersonation.

                The evolution of supply chain security also influenced cybersecurity investment patterns. Venture capital flowed toward startups offering innovative vendor risk management solutions. The market for supply chain security tools grew rapidly, attracting both new entrants and expansion from established cybersecurity vendors seeking to address growing customer demand for comprehensive third-party protection capabilities.

                The legal implications of supply chain breaches created new liability frameworks. Courts began holding organizations responsible for damages caused by vendor negligence, even when the organization itself had implemented reasonable security measures. This expanded liability drove demand for cyber insurance products specifically covering third-party breach scenarios and vendor risk management failures.

                Security awareness training evolved to include vendor risk topics. Employees learned to recognize social engineering attempts targeting vendor relationships and to report suspicious communications from supposed suppliers. This human-centric defense layer complemented technological controls and proved particularly valuable for detecting business email compromise attempts that leveraged vendor impersonation.

                Quantum Computing Breakthroughs 2025: IBM, Google, and the Race Toward Practical Quantum Advantage

                0
                Quantum Computing Breakthroughs 2025: IBM, Google, and the Race Toward Practical Quantum Advantage

                Table of Contents

                  Abstract computing design with geometric patterns representing quantum technology advancement

                  Photo by Google DeepMind via Pexels

                  Introduction: Quantum Computing’s Breakout Year

                  November 2025 marks a watershed for quantum computing. IBM delivered new quantum processors achieving milestones on its path to quantum advantage by end-2026 and fault tolerance by 2029. Google’s Willow chip achieved verifiable quantum advantage, and researchers accomplished the first full simulation of a 50-qubit universal quantum computer. After decades of promises, quantum computing is delivering on revolutionary potential.

                  IBM’s November 2025 Quantum Announcements

                  New Quantum Processors

                  • Improved qubit coherence times
                  • Reduced error rates through enhanced calibration
                  • Circuits exceeding 5,000 quantum gates demonstrated

                  Software Breakthroughs

                  Qiskit 2.0:
                  • Simplified developer experience
                  • Improved error mitigation
                  • Enhanced hybrid quantum-classical workflows
                  • Production-ready application frameworks

                  The Path Forward: IBM’s Roadmap

                  • 2026 Target: Quantum Advantage for practical business problems
                  • 2029 Target: Fault-Tolerant Quantum Computing at scale

                  Google’s Willow Chip: Verifiable Quantum Advantage

                  Technical Specifications

                  • 105 qubits (up from 72 in Sycamore)
                  • 99.9%+ gate fidelity for two-qubit operations
                  • Extended coherence time to microseconds
                  Breakthrough: Below-threshold error correction achieved—as logical qubit size increased, error rate decreased, validating path to fault tolerance.

                  50-Qubit Simulation: Pushing Classical Computing Limits

                  Researchers achieved first full simulation of 50-qubit universal quantum computer, requiring tracking over 1 quadrillion quantum states. Significance: Above 50-60 qubits, quantum computers enter “quantum supremacy” regime where classical simulation becomes infeasible.

                  Practical Applications: When Will Quantum Computing Matter?

                  Near-Term (2025-2027)

                  Quantum Chemistry and Materials Science:
                  • Drug discovery molecular simulation
                  • Battery and catalyst design
                  • Materials property prediction
                  Optimization Problems:
                  • Supply chain and logistics optimization
                  • Financial portfolio optimization
                  • Resource allocation problems

                  Long-Term (2030+)

                  Cryptography Revolution: The Threat: Quantum computers will break current public-key cryptography (RSA, elliptic curve). The Solution: Post-quantum cryptography (PQC) migration must begin now. Timeline: Cryptographically relevant quantum computers estimated 10-15 years away, but organizations must prepare now.

                  The Quantum Race: Global Competition

                  United States Leadership

                  • IBM, Google leading commercial development
                  • Rigetti, IonQ, startups innovating
                  • $1.2+ billion National Quantum Initiative funding

                  Chinese Quantum Ambitions

                  • Optical quantum chip allegedly 1,000x faster than GPUs (claims unverified)
                  • Quantum communication satellite network
                  • Significant state funding

                  European Quantum Efforts

                  • €1 billion Quantum Flagship program
                  • Focus on quantum communications and simulation

                  Investment Landscape: $20 Billion Market in 2025

                  Quantum computing market reached $20 billion in 2025, projected to exceed $100 billion by 2030.

                  Challenges Remaining

                  1. Error Rates and Decoherence

                  Quantum states are fragile; environmental noise disrupts qubits.

                  2. Qubit Count and Quality Trade-off

                  ~100-1,000 qubits in leading systems; millions may be needed for fault tolerance.

                  3. Software and Algorithm Development

                  Quantum algorithms for practical problems remain nascent; talent shortage in quantum algorithm development.

                  4. Cost and Accessibility

                  Single quantum computer: $10-100+ million depending on approach.

                  Conclusion: Quantum Computing’s Inflection Point

                  2025 represents quantum computing’s transition from research to engineering challenge. With IBM targeting practical quantum advantage by end-2026, the timeline for transformative applications is compressing. The Bottom Line:
                  • Quantum computers will complement classical computers for specific problems
                  • Practical applications in chemistry and optimization arriving 2026-2028
                  • Cryptographic threat requires action now
                  • Organizations should begin experimenting for strategic positioning

                  Sources: IBM Newsroom, Harvard Gazette, Google Quantum AI, Live Science, Tom’s Hardware

                  quantum computing breakthroughs 2025 - overview of quantum computing breakthroughs 2025 concepts and framework
                  quantum computing breakthroughs 2025 - quantum computing breakthroughs 2025 implementation and architecture diagram
                  quantum computing breakthroughs 2025 - quantum computing breakthroughs 2025 statistics and key metrics visualization

                  Major Quantum Computing Breakthroughs 2025

                  The year 2025 may be remembered as when quantum computing breakthroughs 2025 moved from theoretical promise to practical milestone. Both established tech giants and nimble startups delivered advances suggesting the quantum advantage era is closer than skeptics predicted.

                  Our comprehensive analysis of quantum computing breakthroughs 2025 reveals progress across hardware fidelity, qubit scaling, error correction, and practical applications. The race toward commercially relevant quantum computing has entered a new phase.

                  IBM’s Quantum Computing Breakthroughs 2025

                  Heron Processor and Beyond

                  IBM’s Heron quantum processor, refined throughout 2025, represents their most capable hardware to date. With 156 qubits and significantly improved gate fidelity, Heron anchored several quantum computing breakthroughs 2025 announcements from IBM’s research division.

                  The key innovation was improved coherence times—qubits maintaining quantum states longer enables deeper circuits and more meaningful computations. Quantum computing breakthroughs 2025 benchmarks showed Heron achieving coherence times exceeding 500 microseconds, a substantial improvement.

                  IBM’s road map released alongside quantum computing breakthroughs 2025 updates projects thousands of qubits with error correction by 2029. The modular architecture approach, connecting multiple Heron processors, demonstrated a viable scaling path during 2025 demonstrations.

                  Qiskit and Software Ecosystem

                  IBM didn’t just advance hardware. Quantum computing breakthroughs 2025 from IBM included significant Qiskit improvements, making quantum programming more accessible. Dynamic circuits, allowing mid-circuit measurement and conditional operations, expanded what algorithms could achieve.

                  The Qiskit ecosystem growth reflects broader quantum computing breakthroughs 2025 trends: software catching up to hardware. Without capable programming frameworks, quantum hardware remains inaccessible. IBM’s investment in developer tooling accelerated practical experimentation.

                  Google’s Quantum Computing Breakthroughs 2025

                  Willow Chip Achievements

                  Google’s Willow quantum chip generated some of the most celebrated quantum computing breakthroughs 2025 headlines. The 105-qubit processor demonstrated exponential error reduction—a critical milestone toward fault-tolerant quantum computing.

                  This error correction achievement is fundamental. Previous quantum computing breakthroughs 2025 struggled with the paradox that adding qubits for error correction introduced more errors than they fixed. Willow demonstrated that scaling can actually reduce errors, validating a core assumption of quantum computing theory.

                  Google’s quantum supremacy claims evolved under quantum computing breakthroughs 2025 scrutiny. While debates continue about practical advantage, Willow’s benchmark performance on specialized problems clearly exceeded classical simulation capabilities.

                  Error Correction Leadership

                  Google’s surface code implementation set the standard for quantum computing breakthroughs 2025 in error correction. Their approach to logical qubits—encoding quantum information across multiple physical qubits—showed the path from noisy intermediate-scale quantum devices to reliable systems.

                  The quantum computing breakthroughs 2025 significance extends beyond raw performance. Google demonstrated that their error correction approach scales, meaning adding more qubits improves rather than degrades system reliability—a prerequisite for building useful quantum computers.

                  The Global Race: Quantum Computing Breakthroughs 2025

                  China’s Quantum Advances

                  China continued its aggressive quantum investments throughout 2025. Chinese quantum computing breakthroughs 2025 included advances in photonic quantum computing and quantum communication networks. The Jiuzhang series processors achieved milestone results in boson sampling.

                  China’s quantum communication satellite network expanded, representing quantum computing breakthroughs 2025 in quantum networking rather than computing. The intercontinental quantum key distribution demonstrated has implications for secure communications globally.

                  European Initiatives

                  The EU’s Quantum Flagship program delivered notable quantum computing breakthroughs 2025 results. European consortia advanced trapped-ion quantum computing, with companies like IQM and Quantinuum achieving significant qubit fidelity improvements.

                  Quantinuum’s trapped-ion systems produced quantum computing breakthroughs 2025 with record-breaking quantum volume metrics. Their H2 system demonstrated capabilities that complement superconducting approaches, suggesting the quantum future may involve multiple architectures rather than one winner.

                  Startup Innovation

                  Beyond the giants, quantum startups contributed substantially to quantum computing breakthroughs 2025. Companies exploring neutral atom, topological, and silicon spin qubit architectures all reported progress, diversifying the approaches being pursued.

                  Atom Computing’s neutral atom system achieved over 1,000 qubits, a quantum computing breakthroughs 2025 milestone demonstrating that alternatives to superconducting qubits can scale rapidly. This diversity of approaches increases the probability that at least one path leads to practical quantum advantage.

                  Practical Applications Emerging from Quantum Computing Breakthroughs 2025

                  Chemistry and Materials Science

                  Quantum simulation remains the most promising near-term application. Quantum computing breakthroughs 2025 in molecular simulation brought drug discovery and materials design closer to quantum-enhanced workflows.

                  Pharmaceutical companies began partnering with quantum hardware providers, recognizing that quantum computing breakthroughs 2025 could eventually accelerate drug development timelines. While current results remain experimental, the trajectory is promising.

                  Optimization Problems

                  Logistics, finance, and supply chain optimization represent large-market applications. Quantum computing breakthroughs 2025 in variational algorithms showed incremental but meaningful improvements over classical methods for specific optimization problem classes.

                  The quantum computing breakthroughs 2025 practical impact remains limited to proof-of-concept demonstrations. However, these demonstrations validate that the theoretical advantages translate to real problems, building confidence for further investment.

                  Cryptography Implications

                  Perhaps the most urgent implication of quantum computing breakthroughs 2025 is the threat to current cryptographic standards. While practical code-breaking quantum computers remain years away, the harvest-now-decrypt-later concern drives post-quantum cryptography adoption.

                  NIST’s post-quantum cryptography standards, finalized and being deployed, represent the response to quantum computing breakthroughs 2025 cryptographic implications. Organizations must begin migration planning now, as the transition is complex and time-consuming.

                  Challenges Ahead After Quantum Computing Breakthroughs 2025

                  Despite the excitement, quantum computing breakthroughs 2025 highlight remaining challenges. Scaling to millions of physical qubits for full error correction remains daunting. Cryogenic infrastructure requirements limit deployment options. Software and algorithm development lags hardware progress.

                  The quantum computing breakthroughs 2025 also raised expectations management concerns. Over-promising practical applications could trigger another quantum winter if near-term results disappoint. Balanced communication about timelines and capabilities is essential.

                  The Road Ahead from Quantum Computing Breakthroughs 2025

                  The momentum from quantum computing breakthroughs 2025 positions the field for accelerated progress. IBM and Google’s error correction advances, combined with diverse architectural approaches from global participants, suggest the next few years will deliver increasingly practical quantum capabilities.

                  For organizations watching from the sidelines, quantum computing breakthroughs 2025 signal that preparation time is ending. Building quantum-ready teams, identifying quantum-relevant use cases, and beginning post-quantum cryptography migration are no longer optional considerations but strategic imperatives for forward-thinking enterprises.

                  Frequently Asked Questions About quantum computing breakthroughs 2025

                  What is quantum computing breakthroughs 2025 and why is it important?

                  Understanding quantum computing breakthroughs 2025 is critical for professionals and organizations navigating today’s rapidly evolving landscape. This topic directly impacts strategic decisions, operational efficiency, regulatory compliance, and long-term competitiveness in the marketplace.

                  How can organizations prepare for quantum computing breakthroughs 2025?

                  Organizations should conduct thorough assessments of their current capabilities, invest in team training and development, develop implementation roadmaps with clear milestones, and establish monitoring systems to track progress. Staying informed about quantum computing breakthroughs 2025 developments ensures proactive rather than reactive responses.

                  What are the main challenges associated with quantum computing breakthroughs 2025?

                  The primary challenges include resource constraints, skill gaps, regulatory compliance requirements, technology integration complexities, and the need for continuous adaptation. However, these challenges also present opportunities for innovation, differentiation, and competitive advantage.

                  How does quantum computing breakthroughs 2025 compare to previous approaches?

                  Compared to earlier methods and frameworks, quantum computing breakthroughs 2025 represents a significant evolution in both scope and impact. The pace of change has accelerated dramatically, requiring more agile, informed, and proactive approaches from all stakeholders involved.

                  What should readers watch for regarding quantum computing breakthroughs 2025?

                  Key indicators to monitor include regulatory developments, market adoption rates, technological breakthroughs, expert analyses, and industry best practices. Subscribing to reputable newsletters and following thought leaders provides valuable ongoing insights.

                  Expert Insights and Strategic Analysis

                  Industry experts and analysts have been closely monitoring developments related to quantum computing breakthroughs 2025, offering valuable perspectives on current trends and future directions that provide additional context and depth.

                  Professional Perspectives

                  Leading professionals emphasize that quantum computing breakthroughs 2025 represents a fundamental shift rather than an incremental change. The implications extend across organizational boundaries, affecting strategy, operations, technology infrastructure, and organizational culture simultaneously.

                  Common Pitfalls to Avoid

                  Several common mistakes can undermine effectiveness when addressing quantum computing breakthroughs 2025. These include underestimating implementation complexity, failing to secure adequate resources, neglecting change management, treating initiatives as one-time projects rather than ongoing programs, and insufficient stakeholder communication.

                  Building a Sustainable Approach

                  Sustainability in the context of quantum computing breakthroughs 2025 requires ongoing commitment, regular reassessment, and adaptive planning. Organizations should establish feedback loops, monitor key performance indicators, and adjust strategies as conditions evolve over time.

                  The Competitive Advantage of Early Adoption

                  Organizations that move quickly to understand and address quantum computing breakthroughs 2025 often gain significant competitive advantages including enhanced reputation, improved operational efficiency, stronger regulatory positioning, and the ability to shape industry standards and best practices.

                  Recommendations for Different Organization Sizes

                  The approach to quantum computing breakthroughs 2025 should vary based on organizational size. Large enterprises can invest in dedicated teams and comprehensive programs. Mid-sized organizations benefit from focused initiatives. Small organizations should prioritize foundational steps and leverage external expertise.

                  Conclusion and Future Outlook

                  This comprehensive analysis of quantum computing breakthroughs 2025 has explored multiple dimensions including current trends, strategic considerations, best practices, risk management, and future outlook. The key takeaway is that quantum computing breakthroughs 2025 demands proactive engagement from organizations of all sizes. By implementing the strategies and recommendations discussed, readers can position themselves effectively. Continuous learning, strategic planning, and adaptive execution remain the cornerstones of success.

                  Deep Dive: Understanding quantum computing breakthroughs 2025 in Practice

                  Real-World Applications and Case Studies

                  Examining real-world applications of quantum computing breakthroughs 2025 reveals practical insights that theoretical frameworks alone cannot provide. Organizations across various sectors have implemented strategies addressing quantum computing breakthroughs 2025 with varying degrees of success. Their experiences offer valuable lessons for others embarking on similar journeys. Case studies demonstrate that success depends on factors including leadership commitment, resource allocation, stakeholder engagement, and adaptation to local conditions.

                  Implementation Framework for quantum computing breakthroughs 2025

                  A structured implementation framework for quantum computing breakthroughs 2025 typically includes several phases. The assessment phase evaluates current state and identifies gaps. The planning phase develops detailed roadmaps with timelines and resource requirements. The execution phase implements planned activities while monitoring progress. The optimization phase refines approaches based on outcomes and feedback. Each phase requires specific competencies and deliverables.

                  Measuring ROI and Impact

                  Demonstrating return on investment for quantum computing breakthroughs 2025 initiatives requires clear metrics and consistent measurement. Quantitative measures might include cost savings, revenue improvements, efficiency gains, and risk reduction. Qualitative indicators encompass stakeholder satisfaction, brand reputation, competitive positioning, and strategic alignment. Organizations should establish baseline measurements before implementation to enable meaningful before-and-after comparisons.

                  Integration with Existing Systems

                  Integrating quantum computing breakthroughs 2025 considerations into existing organizational systems and processes requires careful planning. This includes aligning with current technology infrastructure, incorporating into governance frameworks, embedding into operational procedures, and reflecting in performance metrics. Successful integration minimizes disruption while maximizing value, creating synergies rather than conflicts with established practices.

                  Training and Capability Building

                  Building internal capabilities for managing quantum computing breakthroughs 2025 requires comprehensive training programs. These should address both technical skills and broader competencies including strategic thinking, risk assessment, and change management. Effective programs combine formal training, hands-on experience, mentorship, and continuous learning opportunities. Investment in human capital yields the highest returns for sustainable success.

                  Regulatory and Compliance Considerations

                  The regulatory landscape surrounding quantum computing breakthroughs 2025 continues to evolve, with new requirements emerging regularly. Organizations must maintain awareness of applicable regulations, implement compliance measures, document their efforts, and prepare for potential audits or assessments. Engaging with regulatory bodies and industry associations provides early visibility into upcoming changes and opportunities to shape policy development.

                  Final Thoughts on quantum computing breakthroughs 2025

                  As this analysis demonstrates, quantum computing breakthroughs 2025 is a multifaceted topic that demands comprehensive understanding and strategic response. The organizations and individuals who invest in building knowledge, developing capabilities, and maintaining vigilance will be best positioned to thrive amid ongoing changes. The journey requires commitment, resources, and adaptability, but the potential rewards justify the investment. We encourage readers to continue exploring this topic, engaging with expert communities, and implementing the strategies discussed to achieve their objectives.

                  Additional Resources and Next Steps for quantum computing breakthroughs 2025

                  For readers looking to deepen their understanding of quantum computing breakthroughs 2025, numerous resources are available. Professional certifications offer structured learning paths, while industry conferences provide opportunities for networking and knowledge sharing. Online communities and forums enable peer discussions and problem-solving. Academic research papers and industry reports deliver in-depth analysis for advanced practitioners.

                  Recommended Reading on quantum computing breakthroughs 2025

                  Several authoritative publications regularly cover quantum computing breakthroughs 2025 developments. Subscribing to these sources ensures ongoing awareness of trends, breakthroughs, and best practices. Books by recognized experts provide comprehensive frameworks, while academic journals offer peer-reviewed research findings that validate practical approaches.

                  Taking Action on quantum computing breakthroughs 2025

                  The most effective next step is to assess your organization’s current position relative to quantum computing breakthroughs 2025 and identify priority areas for improvement. Starting with a focused pilot project allows for learning and refinement before broader rollout. Documenting lessons learned and sharing successes builds momentum and organizational support for larger initiatives.

                  Stay informed about quantum computing breakthroughs 2025 by following informbytes.com for regular updates, analysis, and expert commentary on this evolving topic.

                  US-China Tech War 2025: How Geopolitical Tensions Are Reshaping Global Technology Markets

                  0
                  US-China Tech War 2025: How Geopolitical Tensions Are Reshaping Global Technology Markets

                  Table of Contents

                    Detailed globe showcasing Europe and Asia for world geopolitics and technology competition concepts

                    Photo by NastyaSensei via Pexels

                    Introduction: The New Cold War Playing Out in Silicon and Software

                    The US-China technology rivalry has intensified dramatically in 2025, evolving from trade disputes into comprehensive competition for technological supremacy. From semiconductor restrictions to AI development, the world’s two largest economies are locked in an “AI Cold War” with profound implications for global innovation and economic growth.

                    The 2025 Technology Battleground: Key Conflict Areas

                    1. Semiconductor Supremacy: The Foundation of Tech Power

                    US Export Controls Tighten:
                    • Advanced chip manufacturing equipment (EUV lithography) banned
                    • AI-capable GPU exports heavily restricted
                    • Design software and EDA tools require licenses
                    • Outbound investment screening for US capital in Chinese semiconductor firms
                    China’s Response:
                    • $150+ billion committed to domestic chip production
                    • Rare earth export restrictions (gallium, germanium, graphite)
                    • Focus on alternative architectures (chiplets, 3D integration)

                    2. Artificial Intelligence: The Strategic Technology Race

                    DeepSeek’s January 2025 Breakthrough:
                    China’s DeepSeek released an LLM achieving GPT-4-comparable performance using significantly fewer computational resources, demonstrating Chinese AI capabilities advancing despite semiconductor restrictions. US AI Leadership Strategy:
                    • Export controls preventing adversary AI advancement
                    • OpenAI’s $38 billion AWS agreement for massive capacity
                    • Anthropic’s $50 billion U.S. data center buildout

                    Domestic Debates in China: Economic “Involution”

                    Chinese domestic debates reveal concern about economic “involution”—cutthroat competition and unsustainable price wars driven by overcapacity. Manifestations:
                    • E-commerce platforms in subsidy-driven price wars
                    • Local governments racing to subsidize same industries
                    • Companies tolerating losses for market share
                    Geopolitical Connection: With US tariffs threatening exports, Beijing recognizes that economic “involution” risks weakening China’s global competitiveness.

                    Global Impact: Technology Markets Fracture

                    The Emerging Bipolar Technology World

                    Western Ecosystem:
                    • US cloud platforms (AWS, Azure, Google Cloud)
                    • American AI models (OpenAI, Anthropic, Google)
                    • Allied semiconductor supply chains
                    Chinese Ecosystem:
                    • Chinese cloud platforms (Alibaba, Huawei)
                    • Domestic AI models (DeepSeek, Baidu, Alibaba)
                    • Alternative standards and protocols
                    Implications: Multinational corporations face impossible compliance choices as ecosystems diverge.

                    2026 Outlook: What to Expect Next

                    Base Case (60% Probability): Managed Competition

                    • Continued tensions without catastrophic escalation
                    • Strategic decoupling in critical technologies continues
                    • Trade remains substantial despite restrictions

                    Escalation Scenario (25% Probability)

                    • Taiwan contingency triggering comprehensive sanctions
                    • Complete technology decoupling
                    • Economic disruption at pandemic scale

                    Conclusion: Technology Competition Reshaping Global Order

                    The US-China technology war has transcended trade policy to become a defining feature of 21st-century geopolitics. As both nations pursue technological self-sufficiency, the global technology landscape is fracturing into competing ecosystems. Organizations must redesign supply chains with geopolitical resilience, develop scenario planning for multiple futures, and adapt to increasing compliance burdens as regulations proliferate.

                    Sources: Merics, Atlantic Council, ITIF, Wall Street Journal, AEI, El País

                    US China tech war 2025 - overview of US China tech war 2025 concepts and framework
                    US China tech war 2025 - US China tech war 2025 implementation and architecture diagram
                    US China tech war 2025 - US China tech war 2025 statistics and key metrics visualization

                    The Escalation of US China Tech War 2025

                    The global technology landscape underwent fundamental transformation as tensions between the world’s two largest economies reached unprecedented intensity. This comprehensive conflict reshaped semiconductor supply chains, artificial intelligence development, and international trade relationships. Companies worldwide found themselves navigating an increasingly complex geopolitical environment with far-reaching implications.

                    This conflict represented far more than traditional trade disputes. It embodied a fundamental struggle for control over the technologies that will define the next century. Quantum computing, artificial intelligence chips, next-generation telecommunications, and advanced manufacturing all became battlegrounds in this comprehensive technological competition between rival economic systems.

                    Stakes extended beyond economics into national security and global influence. Both nations recognized that technological leadership would determine geopolitical power for decades to come. Consequently, policy decisions made during this period will influence international relations well into the future, affecting alliances, trade patterns, and military capabilities worldwide.

                    Third-party nations faced difficult choices as the conflict intensified. Countries that had maintained neutral technology relationships found themselves pressured to align with one system or the other. This dynamic reshaped diplomatic relationships across Asia, Europe, Africa, and Latin America as technology decisions acquired geopolitical significance they had not previously carried.

                    Key Events Shaping the Technological Rivalry

                    Several pivotal events defined the escalation. The United States expanded entity list restrictions, cutting more Chinese companies from critical technology supply chains. Semiconductor restrictions tightened to include advanced packaging technologies that had previously escaped export control measures, closing loopholes that Chinese firms had exploited.

                    China responded by accelerating domestic chip development programs with massive government-backed investments. State funds poured into local semiconductor manufacturers through multiple funding rounds. The restrictions paradoxically stimulated China’s determination to achieve technological self-sufficiency, potentially reducing long-term effectiveness of export controls as alternative supply chains matured.

                    The conflict also targeted artificial intelligence infrastructure. New restrictions limited Chinese access to advanced GPUs used for training large language models. This move aimed to slow China’s AI military applications while simultaneously affecting commercial AI development across numerous Chinese technology companies and research institutions.

                    Diplomatic tensions spilled into international forums. Both nations competed for influence in standards-setting bodies, trade organizations, and bilateral relationships with third countries. The technological rivalry became a central theme in global diplomacy throughout the year, dominating summit agendas and bilateral meetings that had previously focused on traditional security and trade topics.

                    Space technology emerged as another competition dimension within the ongoing technological conflict. Both nations accelerated satellite deployment programs and lunar exploration missions. Commercial space companies found themselves subject to national security restrictions that limited international collaboration and technology sharing across borders.

                    Semiconductor Restrictions Define the Conflict

                    Semiconductor policy stood at the heart of the technological confrontation. The United States imposed sweeping export controls on advanced chips, manufacturing equipment, and electronic design automation software. These restrictions affected industry leaders including NVIDIA, AMD, ASML, and Applied Materials directly, requiring complex compliance programs and rapid business model adjustments.

                    NVIDIA faced particularly significant challenges. The company had to create modified chip versions specifically for the Chinese market to comply with new regulations. Revenue impacts were substantial, with billions in potential sales at risk. Other semiconductor companies faced similar dilemmas, balancing compliance with revenue preservation while maintaining relationships with Chinese customers.

                    The restrictions created a two-tier global semiconductor market. Advanced chips became available only to approved nations while restricted countries developed alternative supply chains. This bifurcation threatened to fragment the global technology ecosystem that had driven innovation for decades through shared standards and open trade.

                    Equipment manufacturers faced particularly complex restrictions. Lithography machines essential for advanced chip production became diplomatic tools. The Netherlands and Japan, home to critical equipment makers, faced intense diplomatic pressure to align their export controls with American policies, creating tensions within long-standing trade relationships.

                    How the US China Tech War 2025 Reshaped Chip Markets

                    The restrictions fundamentally altered semiconductor market dynamics. Chinese companies stockpiled chips before restrictions took full effect, creating temporary demand surges. Some component categories experienced shortages while others saw overproduction as supply chains adjusted to new realities and companies recalibrated their procurement strategies.

                    Global semiconductor supply chains restructured rapidly. Companies adopted China-plus-one strategies, moving manufacturing operations to Vietnam, India, Malaysia, and Mexico. This diversification required substantial capital investment and years of development to achieve operational maturity comparable to established Chinese facilities that had benefited from decades of investment.

                    Taiwan’s position remained precarious throughout the conflict. As the world’s leading advanced chip manufacturer through TSMC, Taiwan became central to strategic calculations. Both nations increased military and diplomatic posturing in the region, raising concerns about potential supply chain disruption from geopolitical events that could cascade through the global economy.

                    Japanese and South Korean semiconductor companies navigated complex diplomatic pressures. These nations hosted critical links in the semiconductor supply chain but maintained significant economic relationships with both competing powers. Their policy responses influenced the effectiveness of broader restriction frameworks and created diplomatic fault lines.

                    Chip design software became another restriction target within this technological rivalry. Electronic design automation tools from American companies dominated the global market, and restricting Chinese access hampered domestic chip development capabilities. Chinese firms invested heavily in developing alternative design tools, though significant capability gaps remained.

                    Artificial Intelligence as a Primary Battleground

                    Artificial intelligence emerged as a primary front in the rivalry. The United States restricted access to AI training chips while China poured resources into domestic AI development programs. Policies targeted both hardware components and software ecosystems that enabled advanced AI research and commercial deployment across multiple application domains.

                    The AI restrictions affected large language model development directly. Chinese AI companies struggled to obtain sufficient compute resources for training frontier models comparable to Western offerings. Several promising Chinese AI startups pivoted toward more efficient model architectures to compensate for hardware limitations imposed by export controls.

                    Beyond hardware, the conflict extended to AI talent. Both nations implemented policies to attract and retain top AI researchers. Visa restrictions complicated international collaboration in artificial intelligence research, potentially fragmenting the global scientific community that had driven AI progress through open collaboration and knowledge sharing.

                    AI safety and governance approaches diverged significantly. The United States emphasized voluntary commitments and market-driven standards. China implemented strict regulatory requirements with government oversight. These divergent approaches created compliance challenges for multinational companies operating AI systems across both jurisdictions with conflicting requirements.

                    Chinese AI Resilience Despite Restrictions

                    Despite restrictions, Chinese AI companies demonstrated remarkable resilience. Firms like DeepSeek, Alibaba, and Baidu released competitive models using fewer computational resources through innovative training techniques. The restrictions inadvertently drove innovation in efficient AI architectures and training methodologies that might not have emerged otherwise.

                    China’s approach to AI restrictions included massive state investment in domestic GPU development. While Chinese chips initially lagged behind NVIDIA’s offerings in performance, the gap narrowed steadily through targeted investment and engineering talent recruitment. Long-term implications for global AI competition remain uncertain as alternative hardware platforms mature.

                    Chinese researchers also explored alternative computing paradigms including neuromorphic chips and photonic processors. These approaches, if successful, could eventually circumvent restrictions designed around conventional GPU architectures. The innovation response demonstrated how restrictions can stimulate rather than suppress technological development when targeted nations possess sufficient resources.

                    Open source AI models became a contentious area within the US China tech war 2025. Chinese companies released open source models that gained global adoption, raising questions about influence and potential security risks. The open source approach allowed Chinese developers to build international ecosystems around their models despite hardware restrictions.

                    Market Impact Across Global Technology Sector

                    Economic consequences rippled through global markets throughout the year. Technology stocks experienced heightened volatility as policy announcements shifted investor sentiment overnight. Uncertainty caused many companies to delay expansion plans, reduce capital expenditure, and reconsider international strategies that had assumed continued globalization.

                    Chinese technology stocks listed in the United States faced delisting risks under new audit requirements. The potential forced separation of Chinese companies from American capital markets represented a fundamental restructuring of global technology finance. Institutional investors reassessed exposure to companies with significant cross-border dependencies and complex ownership structures.

                    Currency markets also reflected tensions. The Chinese yuan experienced pressure during escalation periods, while the dollar strengthened as a safe haven. These financial dynamics added economic dimensions to what began as technology policy disputes, creating feedback loops between technology restrictions and broader financial market stability.

                    Supply chain costs increased significantly. Companies maintaining parallel supply chains for different markets reported 15-25% higher operational costs. These expenses ultimately passed to consumers through higher technology product prices, making the technological rivalry a tangible economic factor for ordinary citizens worldwide.

                    Technology Companies Navigate Complex Landscape

                    Major technology companies developed sophisticated strategies to navigate the divided landscape. Apple accelerated production shifts to India despite significant manufacturing challenges and quality concerns. Supply chain diversification required substantial capital investment and patient development of new supplier ecosystems capable of meeting quality standards.

                    Cloud providers split their infrastructure to comply with data sovereignty requirements. Microsoft and Amazon maintained separate Chinese cloud regions operated by local partners. This operational complexity increased costs and limited feature parity between regions, affecting customer experience globally and creating competitive disadvantages for affected services.

                    Smaller companies faced disproportionate challenges. Startups with international teams struggled to navigate conflicting regulations. The environment rewarded companies with strong compliance capabilities, legal resources, and deep capital reserves. Many smaller firms exited either the American or Chinese market entirely, reducing global competition and innovation.

                    Geopolitical Dimensions and Global Alliances

                    The US China tech war 2025 extended beyond economics into geopolitics. Allies faced pressure to align with either American or Chinese technology ecosystems. Diplomatic efforts required nations to make difficult choices about telecommunications infrastructure, semiconductor sourcing, and technology standards adoption that would determine their technological trajectories for decades.

                    The Huawei 5G debate intensified as countries that had delayed decisions were forced to choose sides. Several European nations implemented partial bans on Chinese telecommunications equipment. The choices these nations made would influence their technology landscapes for decades given long infrastructure lifecycles and switching costs.

                    The United States strengthened technology alliances through partnerships with Japan, South Korea, and the Netherlands. These relationships proved critical for implementing effective semiconductor restrictions. The diplomatic coordination required represented unprecedented cooperation among allied nations on technology policy and export control harmonization.

                    China cultivated its own partnerships through the Belt and Road Initiative, incorporating digital infrastructure projects across Asia, Africa, and Latin America. Competition extended to developing nations as both powers sought technology influence through investment, training, and infrastructure development that would bind recipient nations to their technology ecosystems.

                    Future Trajectory Beyond 2025

                    Looking beyond the current conflict, decoupling appears increasingly likely. Technology ecosystems may bifurcate into distinct spheres with incompatible standards, separate supply chains, and limited interoperability. The rivalry planted seeds for a fundamentally different global technology landscape that future generations will inherit and navigate.

                    Companies must prepare for continued tensions. Diversified supply chains, robust compliance programs, and scenario planning remain essential capabilities. Geopolitical risk has become a core business consideration rather than a peripheral concern for technology companies worldwide, requiring new organizational competencies and strategic thinking.

                    The US China tech war 2025 will reshape how technology is developed, deployed, and governed worldwide. Organizations that understand these dynamics and adapt proactively will navigate the coming years successfully. Those that ignore geopolitical realities face significant operational and strategic risks as the divided landscape evolves and new fault lines emerge between competing technology spheres.

                    Ultimately, this technological rivalry may accelerate innovation in both nations while fragmenting the global cooperation that has historically driven scientific progress. The balance between competitive stimulation and collaborative loss will define the trajectory of global technology development for decades to come, making this period a watershed moment in international technology relations.

                    Emerging Technologies and Future Competition

                    Beyond semiconductors and AI, the rivalry extended to emerging technologies with long-term strategic implications. Quantum computing research became a focal point, with both nations investing heavily in quantum advantage development. The first nation to achieve practical quantum computing would gain unprecedented capabilities in cryptography, materials science, and optimization problems with military applications.

                    Biotechnology emerged as another competition frontier. Genomic editing, synthetic biology, and pharmaceutical development all received increased government funding and strategic priority. Both nations recognized that biotechnology leadership would determine healthcare independence and potential military biodefense capabilities for decades to come.

                    Quantum communication networks represented a particular area of Chinese investment. China launched quantum satellites and developed ground-based quantum networks ahead of American efforts. This leadership in quantum communication could provide advantages in secure military communications that traditional encryption cannot guarantee against future quantum computing threats.

                    The rivalry also extended to clean energy technologies. Solar panel manufacturing, battery technology, and electric vehicle development all became arenas of competition. Chinese dominance in solar manufacturing created dependencies that Western nations sought to reduce through alternative supply chains and domestic production incentives despite significant cost disadvantages.

                    Autonomous systems competition intensified across multiple domains. Self-driving vehicle technology, autonomous maritime vessels, and drone swarms all received strategic investment from both nations. Military applications of autonomous systems created particular concern, as the nation achieving breakthrough capabilities could fundamentally alter battlefield dynamics in future conflicts.

                    Cloud Security Best Practices 2025: Complete Guide to AWS, Azure, and GCP

                    0
                    Cloud Security Best Practices 2025: Complete Guide to AWS, Azure, and GCP

                    Table of Contents

                      Modern server unit in blue-lit data center environment representing cloud security infrastructure Photo by panumas nikhomkhai via Pexels

                      Introduction: The Critical Importance of Cloud Security in 2025

                      As organizations continue migrating critical workloads to cloud environments, cloud security has evolved from a technical consideration to a business imperative. With over 90% of enterprises now using multi-cloud strategies and cyber threats growing in sophistication, implementing comprehensive cloud security best practices is no longer optional. The stakes have never been higher. Data breaches in cloud environments can cost organizations millions in remediation, regulatory fines, and reputational damage.

                      Understanding the Cloud Shared Responsibility Model

                      What Cloud Providers Secure (Security OF the Cloud)

                      • Physical infrastructure security (data centers, hardware, facilities)
                      • Networking infrastructure (routers, switches, load balancers)
                      • Virtualization layer (hypervisors, host OS)
                      • Managed services infrastructure

                      What Customers Must Secure (Security IN the Cloud)

                      • Identity and Access Management (IAM) configurations
                      • Data encryption (at rest and in transit)
                      • Network security controls (firewalls, security groups)
                      • Application security
                      • Compliance with regulations
                      Critical Insight: Most cloud security breaches result from customer misconfigurations, not cloud provider failures.

                      Foundational Cloud Security Principles

                      1. Zero Trust Architecture

                      Zero Trust operates on: “Never trust, always verify.” Core Zero Trust Principles:
                      • Verify explicitly: Authenticate and authorize based on all available data
                      • Least privileged access: Grant minimum necessary permissions
                      • Assume breach: Minimize blast radius and segment access
                      • Continuous monitoring: Real-time security analytics

                      2. Defense in Depth

                      Layer multiple security controls:
                      • Network security: Firewalls, security groups, network ACLs
                      • Identity security: MFA, conditional access, privileged access management
                      • Data security: Encryption, tokenization, data loss prevention
                      • Application security: WAF, API gateways, runtime protection
                      • Monitoring: SIEM, log aggregation, threat intelligence

                      Identity and Access Management (IAM) Best Practices

                      IAM is the cornerstone of cloud security. Compromised credentials remain a leading attack vector.

                      AWS Identity and Access Management

                      Key Recommendations:
                      • Implement least privilege access policies
                      • Use IAM roles instead of access keys
                      • Enable MFA for all users
                      • Use AWS Organizations with Service Control Policies
                      • Deploy GuardDuty for threat detection
                      • Use IAM Access Analyzer for policy review

                      Microsoft Azure Active Directory and RBAC

                      Key Recommendations:
                      • Implement Azure AD Conditional Access
                      • Deploy Privileged Identity Management (PIM)
                      • Use Azure RBAC with least privilege
                      • Enable Managed Identities for applications
                      • Deploy Microsoft Defender for Cloud

                      Google Cloud Identity and Access Management

                      Key Recommendations:
                      • Use Cloud IAM hierarchy effectively
                      • Implement short-lived service account keys
                      • Deploy VPC Service Controls
                      • Use Policy Intelligence tools
                      • Enable Security Command Center

                      Network Security Best Practices

                      Virtual Private Cloud (VPC) Security

                      1. Network Segmentation Design VPCs with security zones:
                      • Public subnets: Internet-facing load balancers, bastion hosts
                      • Private subnets: Application servers, business logic
                      • Isolated/data subnets: Databases, data warehouses
                      • Management subnet: Security tools, logging infrastructure
                      2. Security Groups Best Practices
                      • Default deny all; explicitly allow required traffic
                      • Reference security groups rather than IP ranges
                      • Regular security group audits
                      • Document security group purpose
                      3. Private Endpoints
                      • AWS PrivateLink, Azure Private Endpoints, Google Cloud Private Service Connect
                      • Access cloud services without internet exposure
                      • Prevent data exfiltration risks

                      Data Encryption and Protection

                      Encryption at Rest

                      Enable Default Encryption for All Storage: AWS:
                      • S3: Enable default bucket encryption (SSE-KMS)
                      • EBS: Enable volume encryption by default
                      • RDS: Enable storage encryption for databases
                      Azure:
                      • Blob Storage: Storage Service Encryption
                      • Azure SQL: Transparent Data Encryption (TDE)
                      • Managed Disks: Azure Disk Encryption
                      Google Cloud:
                      • Cloud Storage: Automatic encryption at rest
                      • Compute Engine: Encrypted persistent disks
                      • Cloud SQL: Automatic data encryption

                      Customer-Managed Encryption Keys

                      • AWS KMS: Customer Master Keys with rotation
                      • Azure Key Vault: Key management with HSM options
                      • Google Cloud KMS: Centralized cryptographic key management

                      Cloud Security Monitoring and Incident Response

                      Centralized Logging and SIEM

                      AWS Logging:
                      • CloudTrail: API activity logging
                      • CloudWatch Logs: Application and infrastructure logs
                      • VPC Flow Logs: Network traffic logging
                      • GuardDuty Findings: Threat detection alerts
                      Azure Logging:
                      • Activity Logs: Subscription-level operations
                      • Diagnostic Logs: Resource-level operations
                      • Microsoft Sentinel: Cloud-native SIEM
                      Google Cloud Logging:
                      • Cloud Audit Logs: Admin activity and data access
                      • Cloud Logging: Unified logging service
                      • Security Command Center: Centralized security findings

                      Common Cloud Security Mistakes to Avoid

                      1. Overly Permissive IAM Policies – Grant minimum necessary access
                      2. Unencrypted Data Storage – Enable encryption at rest everywhere
                      3. Publicly Exposed Resources – Regular scanning for public exposure
                      4. Insufficient Logging – Centralized logging is mandatory
                      5. Lack of Network Segmentation – Multi-tier architecture required
                      6. Ignoring Shared Responsibility – Understand what YOU must secure
                      7. No Incident Response Plan – Written procedures are essential
                      8. Poor Secrets Management – Use cloud-native secrets services

                      Cloud Security Implementation Roadmap

                      Month 1: Foundational Security

                      • Enable MFA for all accounts
                      • Implement least privilege IAM
                      • Enable comprehensive logging
                      • Enable default encryption
                      • Configure security groups with deny-by-default

                      Month 2: Enhanced Controls

                      • Implement private endpoints
                      • Deploy Web Application Firewall
                      • Enable vulnerability scanning
                      • Set up SIEM/security analytics
                      • Configure automated alerting

                      Month 3: Advanced Security

                      • Implement Infrastructure as Code security
                      • Deploy automated remediation
                      • Establish Zero Trust architecture
                      • Conduct incident response exercises

                      Conclusion: Cloud Security as Continuous Journey

                      Cloud security is not a one-time implementation but a continuous journey requiring ongoing attention, adaptation, and improvement. As threats evolve and cloud platforms introduce new services, security strategies must evolve in parallel. Key Principles for Success:
                      • Adopt Zero Trust architecture
                      • Automate security controls relentlessly
                      • Monitor continuously with centralized logging
                      • Embrace shared responsibility model
                      • Prioritize data encryption and access controls
                      Organizations that treat cloud security as strategic priority will be best positioned to leverage cloud benefits while managing risks effectively.
                      Sources: Microsoft Learn Azure Security Benchmark, AWS Well-Architected Framework, Google Cloud Security Documentation, Cloud Security Alliance
                      cloud security best practices 2025 - overview of cloud security best practices 2025 concepts and framework
                      cloud security best practices 2025 - cloud security best practices 2025 implementation and architecture diagram
                      cloud security best practices 2025 - cloud security best practices 2025 statistics and key metrics visualization

                      Cloud Security Best Practices 2025: Securing the Modern Enterprise

                      Cloud security best practices 2025 have evolved significantly as organizations move critical workloads to AWS, Azure, and Google Cloud Platform. The shared responsibility model, once a simple delineation of duties, now requires nuanced understanding as cloud services multiply and configurations grow complex. Getting security right demands a systematic approach.

                      The cloud security best practices 2025 framework must address the reality that most organizations now operate in multi-cloud environments. Each provider has different security tools, terminology, and default configurations. Developing practices that work across providers while leveraging each platform’s native capabilities is the central challenge for security teams.

                      Identity and Access in Cloud Security Best Practices 2025

                      Identity and access management sits at the core of cloud security best practices 2025. In cloud environments, identity is the new perimeter. Without physical network boundaries to defend, controlling who can access what becomes the primary security mechanism. Robust identity governance is non-negotiable.

                      Cloud security best practices 2025 for identity include implementing least-privilege access, requiring multi-factor authentication for all accounts, and regularly reviewing permissions. Many cloud breaches result from over-privileged accounts or compromised credentials. Tightening access reduces the attack surface dramatically.

                      Privileged access management deserves special attention in cloud security best practices 2025. Administrative accounts with broad permissions represent the highest-risk identities. Implementing just-in-time access, where privileges are granted temporarily and revoked automatically, minimizes the window of exposure for compromised admin credentials.

                      Encryption Strategies in Cloud Security Best Practices 2025

                      Encryption is fundamental to cloud security best practices 2025. Data should be encrypted at rest and in transit as a baseline. But modern cloud environments require more sophisticated approaches, including encryption in use through confidential computing and customer-managed keys for sensitive workloads.

                      Cloud security best practices 2025 for key management emphasize the importance of controlling your own encryption keys. While cloud providers offer managed encryption services, using provider-managed keys means the provider can access your data. Customer-managed keys, stored in hardware security modules, provide stronger isolation.

                      Data classification informs encryption priorities within cloud security best practices 2025. Not all data requires the same level of protection. By classifying data by sensitivity, organizations can apply encryption and access controls proportionally, focusing resources on the most valuable and regulated data.

                      Monitoring and Detection in Cloud Security Best Practices 2025

                      Continuous monitoring is a pillar of cloud security best practices 2025. Cloud environments are dynamic, with resources created and destroyed continuously. Traditional point-in-time security assessments miss changes that occur between scans. Real-time monitoring with cloud-native tools like AWS GuardDuty, Azure Sentinel, or GCP Security Command Center is essential.

                      Cloud security best practices 2025 for monitoring include log aggregation across all cloud services, automated alerting on anomalous activity, and regular review of security findings. The volume of security telemetry in cloud environments can be overwhelming, so prioritization and automated triage are critical capabilities.

                      Configuration monitoring deserves specific attention in cloud security best practices 2025. Misconfigurations are the leading cause of cloud breaches. Tools that continuously assess configurations against security benchmarks catch drift before it becomes a vulnerability. Automated remediation can fix many issues without human intervention.

                      Compliance and Cloud Security Best Practices 2025

                      Compliance requirements shape cloud security best practices 2025 for most organizations. Regulations like GDPR, HIPAA, PCI DSS, and industry-specific requirements dictate specific security controls. Cloud environments can complicate compliance, but they also offer tools to automate compliance monitoring and reporting.

                      Cloud security best practices 2025 for compliance include mapping cloud controls to regulatory requirements, maintaining documentation of control implementation, and conducting regular compliance assessments. Cloud providers offer compliance certifications and attestations that organizations can leverage to demonstrate their security posture.

                      The cloud security best practices 2025 approach to compliance also involves data residency considerations. Regulations may require that certain data remains within specific geographic boundaries. Cloud providers offer regional services, but organizations must configure their deployments correctly to ensure compliance with data residency requirements.

                      Multi-Cloud Considerations in Cloud Security Best Practices 2025

                      Many organizations operate across AWS, Azure, and GCP, and cloud security best practices 2025 must address this reality. A consistent security posture across providers requires understanding each platform’s native tools while establishing common policies and standards that apply everywhere.

                      Cloud security best practices 2025 for multi-cloud environments include using cloud security posture management tools that work across providers. These tools provide a unified view of security configurations, vulnerabilities, and compliance status, reducing the complexity of managing security across multiple clouds.

                      Network security across clouds is another consideration in cloud security best practices 2025. Connecting cloud environments securely requires careful design of network peering, VPN connections, and traffic filtering. Consistent network security policies across providers prevent gaps that adversaries could exploit.

                      DevSecOps and Cloud Security Best Practices 2025

                      Integrating security into the development lifecycle is a key component of cloud security best practices 2025. DevSecOps embeds security checks into CI/CD pipelines, catching vulnerabilities before they reach production. This shift-left approach is more effective and less costly than post-deployment security testing.

                      Cloud security best practices 2025 for DevSecOps include infrastructure-as-code scanning, container image vulnerability scanning, and automated security testing of applications. By making security a continuous part of the development process rather than a gate at the end, organizations build security in rather than bolting it on.

                      Policy as code is an emerging cloud security best practices 2025 approach. By expressing security policies in code, organizations can automate enforcement and provide immediate feedback to developers when their configurations violate policies. This approach makes security both more reliable and more developer-friendly.

                      Incident Response in Cloud Security Best Practices 2025

                      Cloud security best practices 2025 extend to incident response. Cloud environments require different response procedures than on-premises systems. The ability to rapidly isolate compromised resources, preserve forensic evidence in ephemeral environments, and coordinate response across cloud and on-premises systems is essential.

                      Cloud security best practices 2025 for incident response include developing cloud-specific playbooks, conducting regular tabletop exercises, and establishing communication channels with cloud providers’ security teams. Many breaches are detected and contained faster when organizations have pre-established relationships with provider security teams.

                      The cloud security best practices 2025 landscape will continue evolving as new services and threats emerge. Organizations that build flexible, automated, and well-documented security programs will adapt most effectively. The goal is not a fixed state of security but a continuous process of improvement that keeps pace with the changing cloud landscape.

                      Frequently Asked Questions About cloud security best practices 2025

                      What is cloud security best practices 2025 and why does it matter?

                      Understanding cloud security best practices 2025 is essential for professionals and businesses navigating today’s rapidly evolving landscape. This topic directly impacts strategic decisions, operational efficiency, and long-term competitiveness.

                      How can organizations prepare for changes related to cloud security best practices 2025?

                      Organizations should conduct thorough assessments, invest in training, and develop implementation roadmaps. Staying informed about cloud security best practices 2025 developments ensures proactive rather than reactive responses.

                      What are the key challenges associated with cloud security best practices 2025?

                      The primary challenges include resource constraints, skill gaps, regulatory compliance, and the need for continuous adaptation. However, these challenges also present opportunities for innovation and differentiation.

                      How does cloud security best practices 2025 compare to previous trends in this space?

                      Compared to earlier developments, cloud security best practices 2025 represents a significant evolution in both scope and impact. The pace of change has accelerated, requiring more agile and informed approaches.

                      What should readers watch for regarding cloud security best practices 2025 in the coming months?

                      Key indicators to monitor include regulatory developments, market adoption rates, technological breakthroughs, and expert analyses. Subscribing to industry newsletters and following thought leaders provides valuable ongoing insights.

                      Are there specific tools or resources recommended for cloud security best practices 2025?

                      Yes, several industry-standard tools and frameworks can help organizations navigate cloud security best practices 2025. Research reports, professional certifications, and community forums offer practical guidance and peer support.

                      In-Depth Analysis: cloud security best practices 2025 Implications and Strategies

                      Strategic Considerations for cloud security best practices 2025

                      Organizations navigating cloud security best practices 2025 must develop comprehensive strategies that address both immediate needs and long-term objectives. This requires cross-functional collaboration, executive-level commitment, and ongoing investment in capabilities and infrastructure. The most successful approaches balance innovation with risk management, ensuring sustainable progress.

                      Industry Best Practices for cloud security best practices 2025

                      Leading organizations have identified several best practices for managing cloud security best practices 2025 effectively. These include establishing clear governance structures, investing in employee training and development, leveraging technology solutions strategically, and maintaining open communication with stakeholders. Regular assessment and adjustment of strategies ensures continued alignment with evolving conditions.

                      Risk Management and cloud security best practices 2025

                      Effective risk management in the context of cloud security best practices 2025 requires identifying potential threats, assessing their likelihood and impact, developing mitigation strategies, and establishing monitoring systems. Organizations should create contingency plans for various scenarios and regularly test their preparedness through simulations and exercises.

                      Conclusion

                      The landscape of cloud security best practices 2025 continues to evolve rapidly, presenting both challenges and opportunities. By understanding the key dynamics, implementing effective strategies, and maintaining vigilance, organizations can navigate this terrain successfully. The insights provided in this analysis offer a comprehensive foundation for informed decision-making and strategic planning.

                      Expert Insights and Analysis on cloud security best practices 2025

                      Industry experts and analysts have been closely monitoring developments related to cloud security best practices 2025, offering valuable perspectives on current trends and future directions. Their insights provide additional context and depth to understanding this evolving landscape.

                      Professional Perspectives on cloud security best practices 2025

                      Leading professionals in the field emphasize that cloud security best practices 2025 represents a fundamental shift rather than an incremental change. The implications extend across organizational boundaries, affecting strategy, operations, technology, and culture. Organizations that recognize and respond to these shifts proactively gain significant advantages over those that adopt a wait-and-see approach.

                      Common Pitfalls to Avoid with cloud security best practices 2025

                      Several common mistakes can undermine effectiveness when addressing cloud security best practices 2025. These include underestimating the complexity of implementation, failing to secure adequate resources, neglecting change management, and treating initiatives as one-time projects rather than ongoing programs. Learning from the experiences of early adopters helps organizations avoid these pitfalls and achieve better outcomes.

                      Building a Sustainable Approach to cloud security best practices 2025

                      Sustainability in the context of cloud security best practices 2025 requires ongoing commitment, regular reassessment, and adaptive planning. Organizations should establish feedback loops, monitor key indicators, and adjust strategies as conditions evolve. This approach ensures that efforts remain relevant and effective over time, rather than becoming outdated as the landscape shifts.

                      The Competitive Advantage of Early Adoption

                      Organizations that move quickly to understand and address cloud security best practices 2025 often gain significant competitive advantages. These benefits include enhanced reputation, improved operational efficiency, stronger regulatory positioning, and the ability to shape industry standards. While early adoption carries risks, the potential rewards substantially outweigh the costs of delayed action.

                      Recommendations for Different Organizational Sizes

                      The approach to cloud security best practices 2025 should vary based on organizational size and resources. Large enterprises can invest in dedicated teams and comprehensive programs. Mid-sized organizations benefit from focused initiatives targeting high-impact areas. Small organizations should prioritize foundational steps and leverage external expertise and resources to maximize limited budgets.

                      Conclusion: Key Takeaways on cloud security best practices 2025

                      This comprehensive analysis of cloud security best practices 2025 has explored multiple dimensions including current trends, strategic considerations, best practices, risk management, and future outlook. The key takeaway is that cloud security best practices 2025 demands proactive engagement from organizations of all sizes. By implementing the strategies and recommendations discussed, readers can position themselves effectively amid ongoing changes. Continuous learning, strategic planning, and adaptive execution remain the cornerstones of success in this dynamic environment.